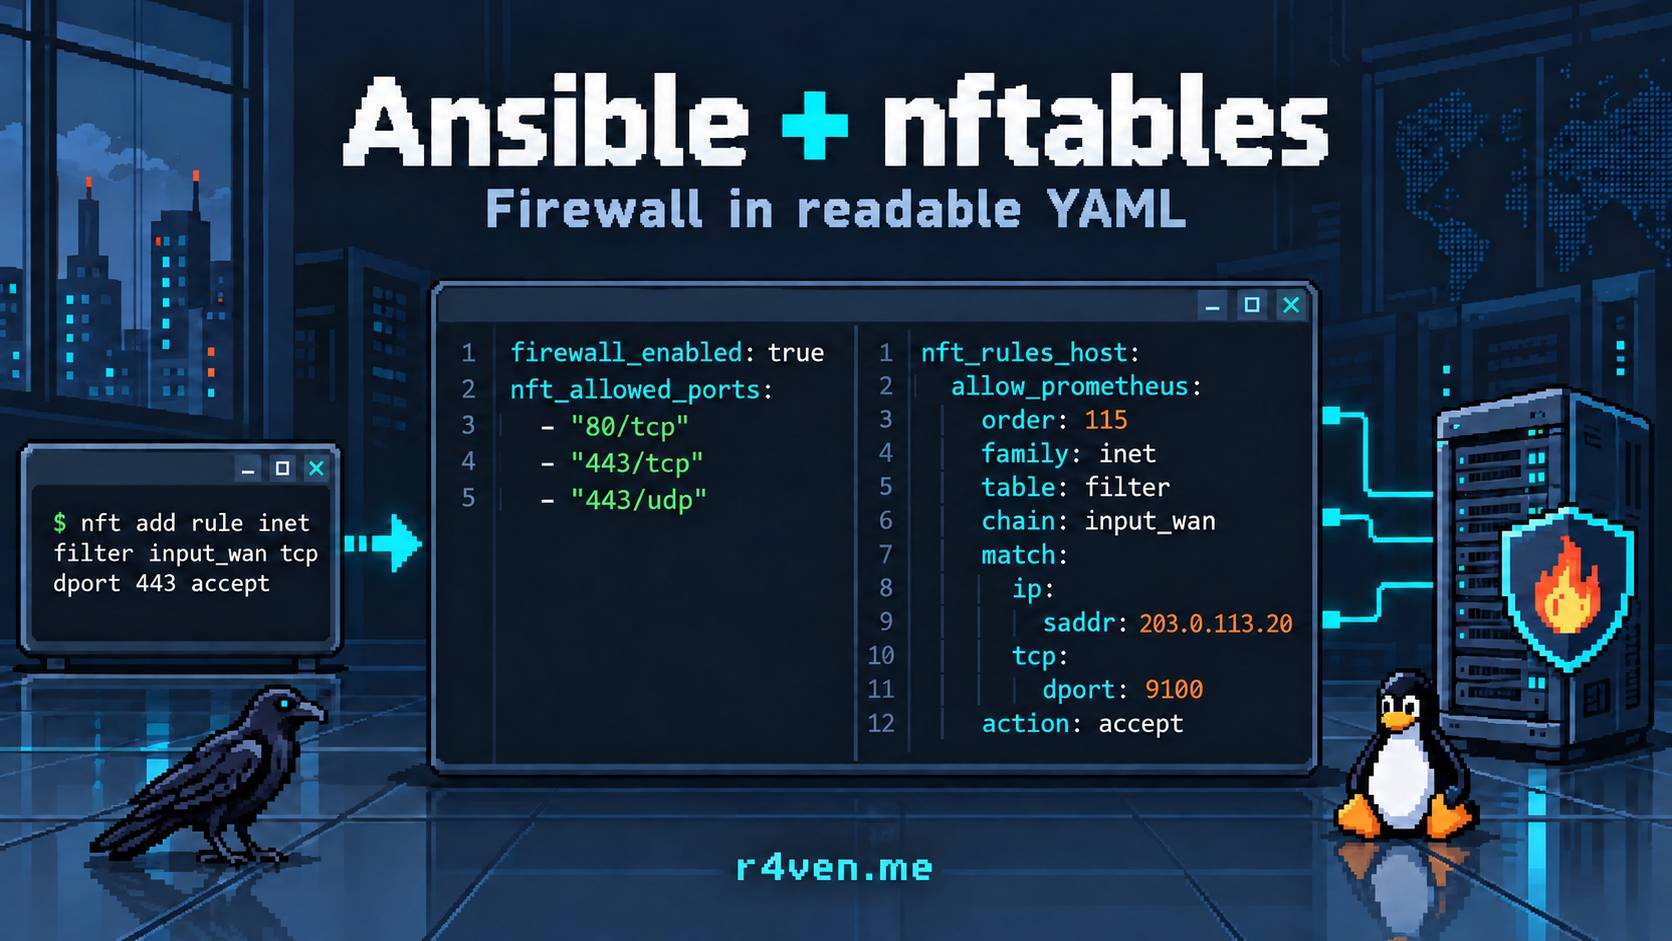
Ansible: managing an nftables firewall with the firewall role
A look at my Ansible firewall role for managing nftables: rules as YAML, a base policy for the whole server fleet, per-host exceptions, and protection against losing SSH access when rules are applied.