See how to configure convenient search and launch of terminal commands and SSH sessions in Tmux using the FZF plugin under the spoiler:
Spoiler :)
Let me remind you right away that by default the prefix key in Tmux is the Ctrl-b key combination⌨️
Option No. 1 - installing my tmux configuration
Prerequisites:
- Any monospace icon Powerline font⚡️, for example from the Nerd fonts project. I prefer Hack Nerd Font Mono. The font must be placed in
/usr/share/fonts/or separately for the user in~/.local/share/fonts/and applied to the terminal; - Any terminal emulator🧑💻 with TrueColor support and the Nord theme, for example Gnome-terminal or Guake;
- (Optional) An interactive command shell💻, for example Zsh + Oh-My-Zsh with the agnoster theme.
Installing the config from my GitHub:
sudo apt update && sudo apt install -y git xclip fzf tmux

git clone https://github.com/r4ven-me/tmux.git ~/.config/tmux

tmux new -s WorkThe first launch will take some time.
Check command/session search with the keys.
Option No. 2 - installing and configuring the FZF plugin separately
Install the required utilities:
sudo apt update && sudo apt install -y git xclip fzf tmuxOpen the config for editing:
mkdir -p ~/.config/tmux/

nvim ~/.config/tmux/tmux.confInsert the following code:
# FZF parameters
set-environment -g TMUX_FZF_OPTIONS "-p -w 65% -h 35% -m"

# Quick commands via prefix+Ctrl-b
bind-key C-b run-shell "
    command_list="~/.config/tmux/commands.list"
    command=\$(cat \$command_list | fzf-tmux \$TMUX_FZF_OPTIONS --reverse --prompt=\"⚡️ Command: \") && \
    tmux send-keys \"\${command#*] }\" || \
    exit 0
"

# Quick SSH session launch from ~/.ssh/config via prefix+Shift-b
bind-key B run-shell "
    host=\$(grep -E \"^Host \" ~/.ssh/config | sed \"s/^Host //\" | fzf-tmux \$TMUX_FZF_OPTIONS --reverse --prompt=\"🌐 SSH: \") && \
    tmux new-window -n \"SSH [\$host\"] \"ssh \$host\" || \
    exit 0
"

# FZF plugin activation
set -g @plugin 'sainnhe/tmux-fzf'

# this line must be the last one!
run '~/.config/tmux/plugins/tpm/tpm'Create a commands.list file with the list of required commands:
nvim ~/.config/tmux/commands.listSpecify commands line by line. Example:
LINES='6'; ps --sort=-%cpu -eo user,pid,ppid,state,comm | head -n "$LINES"
LINES='6'; ps --sort=-%mem -eo user,pid,ppid,state,comm | head -n "$LINES"
DIR='/'; LIMIT='20'; du -h "$DIR" 2> /dev/null | sort -rh | head -n "$LIMIT"If you want to add a comment to a command, put it in square brackets before the command itself, followed by a space. Example:
[ps top5 cpu] LINES='6'; ps --sort=-%cpu -eo user,pid,ppid,state,comm | head -n "$LINES"
[ps top5 mem] LINES='6'; ps --sort=-%mem -eo user,pid,ppid,state,comm | head -n "$LINES"
[du top20] DIR='/'; LIMIT='20'; du -h "$DIR" 2> /dev/null | sort -rh | head -n "$LIMIT"Now install the tpm package manager and start installing the FZF plugin:
git clone https://github.com/tmux-plugins/tpm ~/.config/tmux/plugins/tpm

tmux new -s Work '~/.config/tmux/plugins/tpm/bin/install_plugins'Done. Create a new session:
tmux new -s WorkIf you need to set additional FZF parameters, this is done through the special TMUX_FZF_OPTIONS environment variable.
Earlier, we already set it directly in the tmux config.
For example, the following values set custom popup size parameters and the Nord color palette:
set-environment -g TMUX_FZF_OPTIONS "
    -p -w 65% -h 35% -m
    --exact
    --color=fg:#e5e9f0,bg:#2e3440,hl:#81a1c1
    --color=fg+:#e5e9f0,bg+:#2e3440,hl+:#81a1c1
    --color=info:#eacb8a,prompt:#bf6069,pointer:#b48dac
    --color=marker:#a3be8b,spinner:#b48dac,header:#a3be8b
    --color=border:#5e81ac
    --border=rounded
"Check command/session search with the keys.
prefix+Ctrl-b(commands):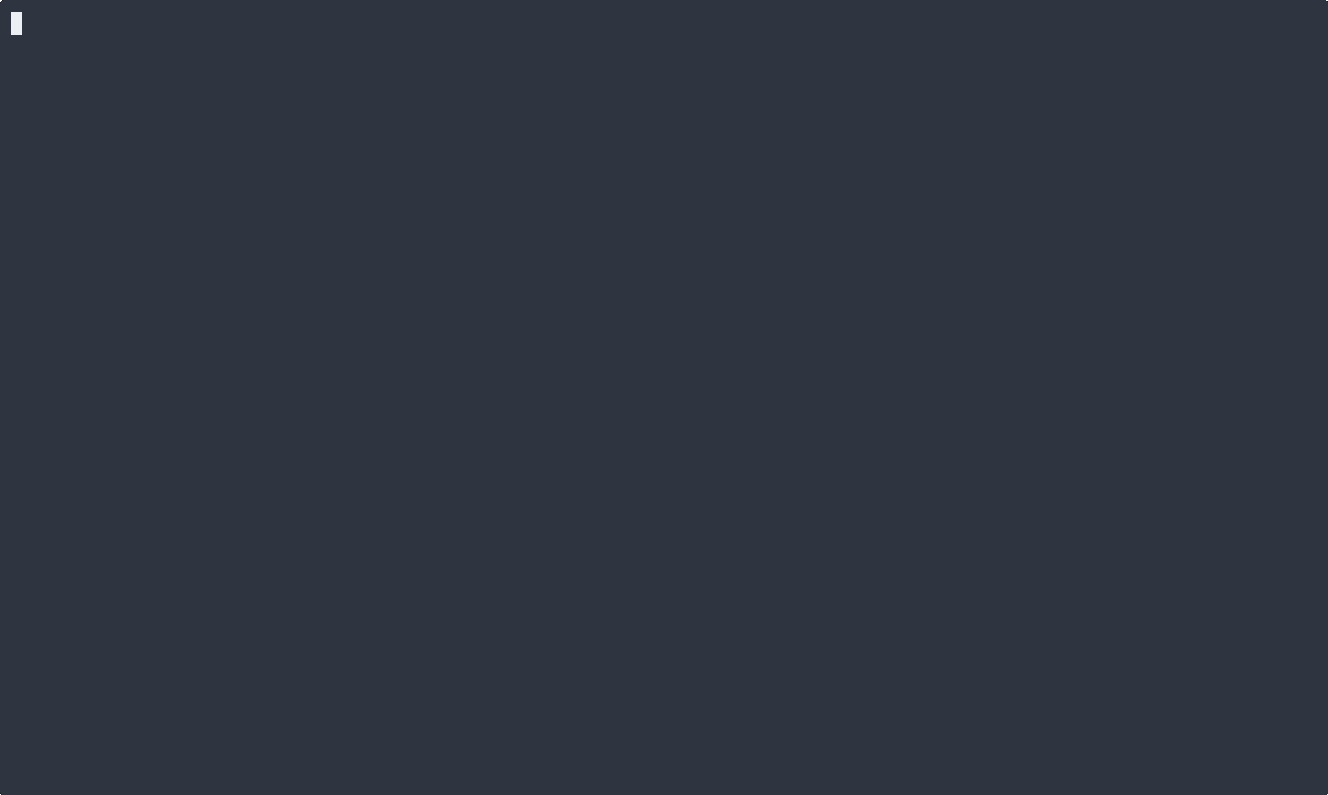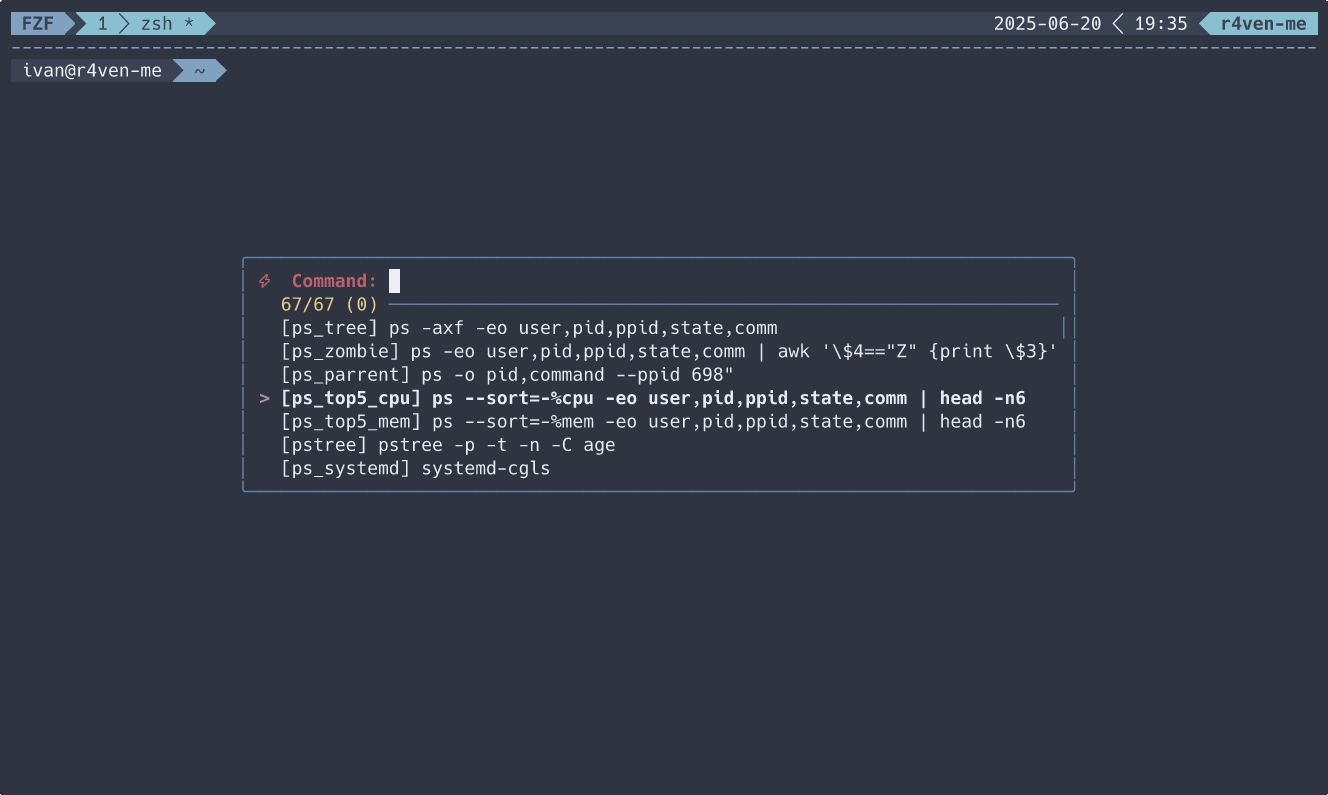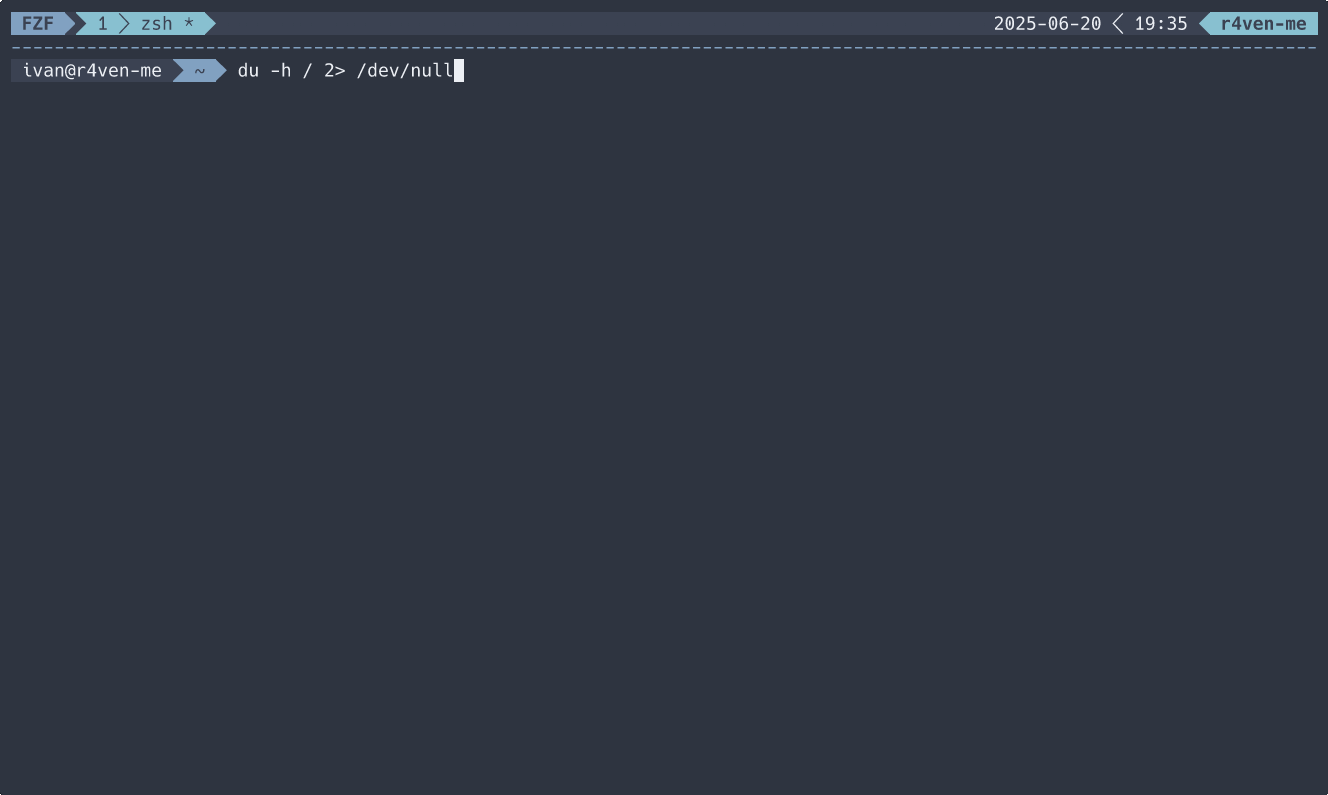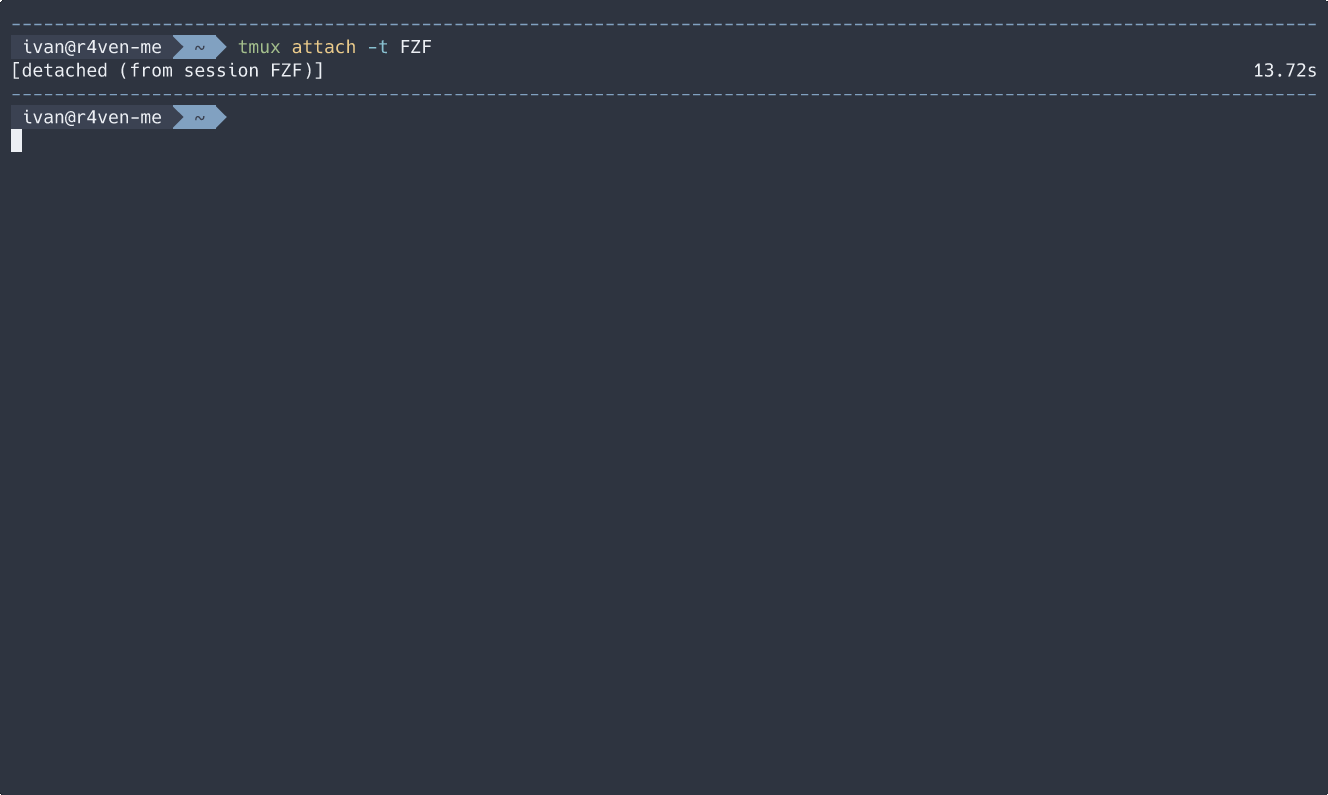
💡The command list from the collection in the required format is available on GitHub.
prefix+Shift-b(SSH hosts):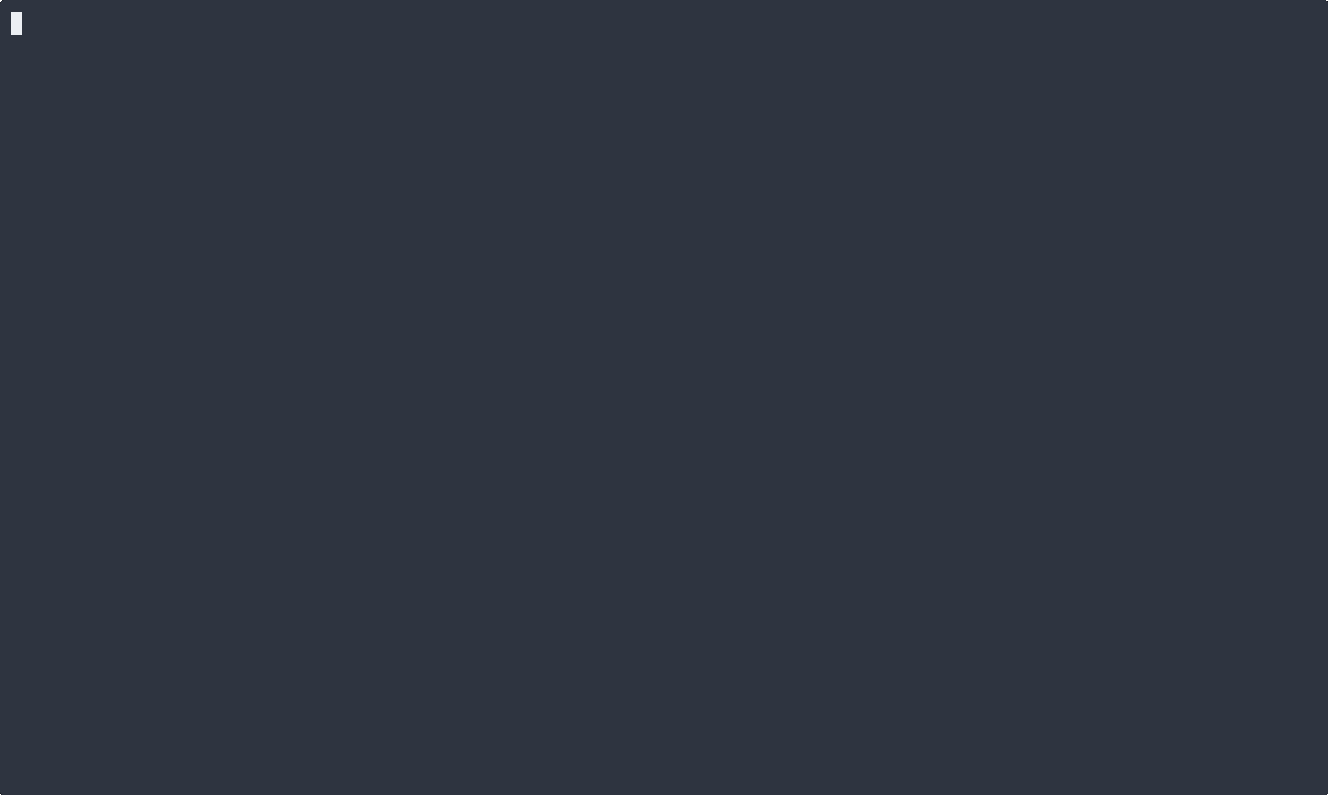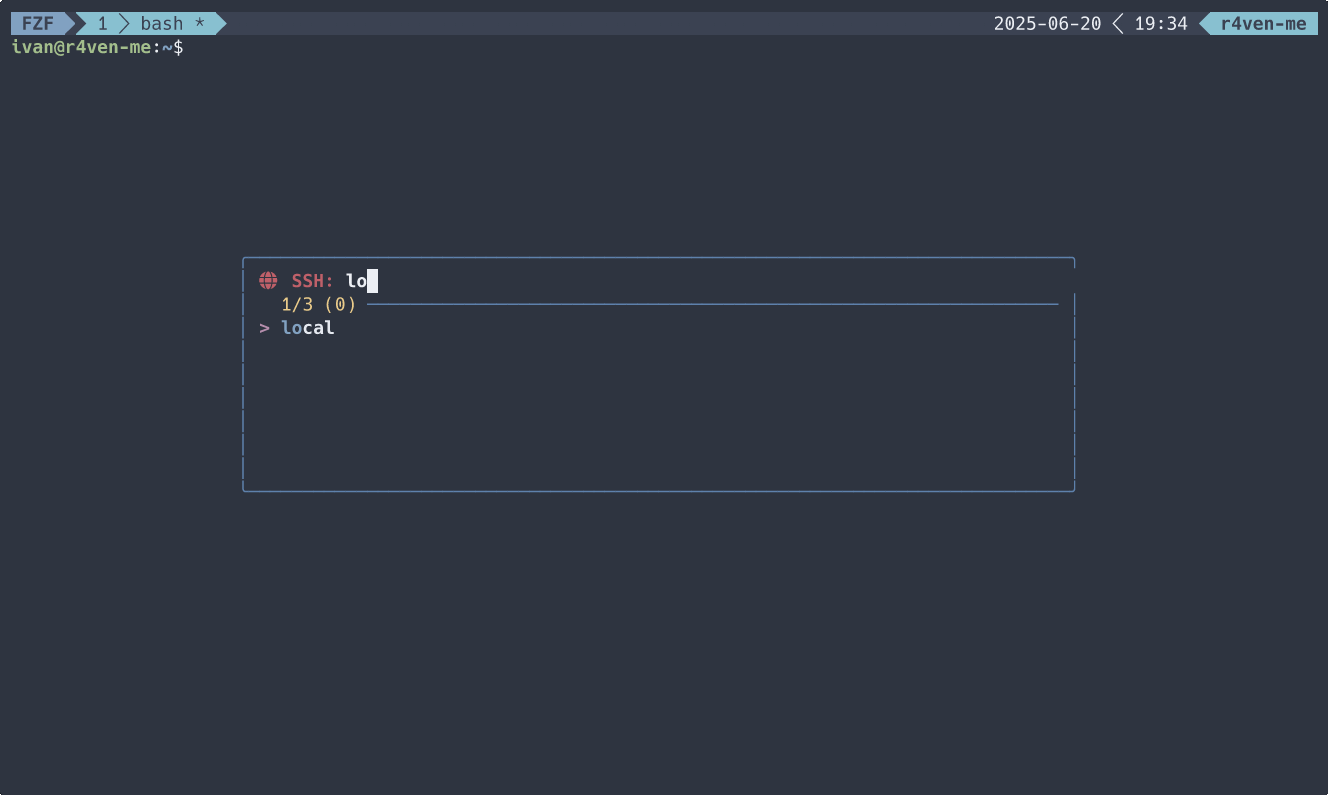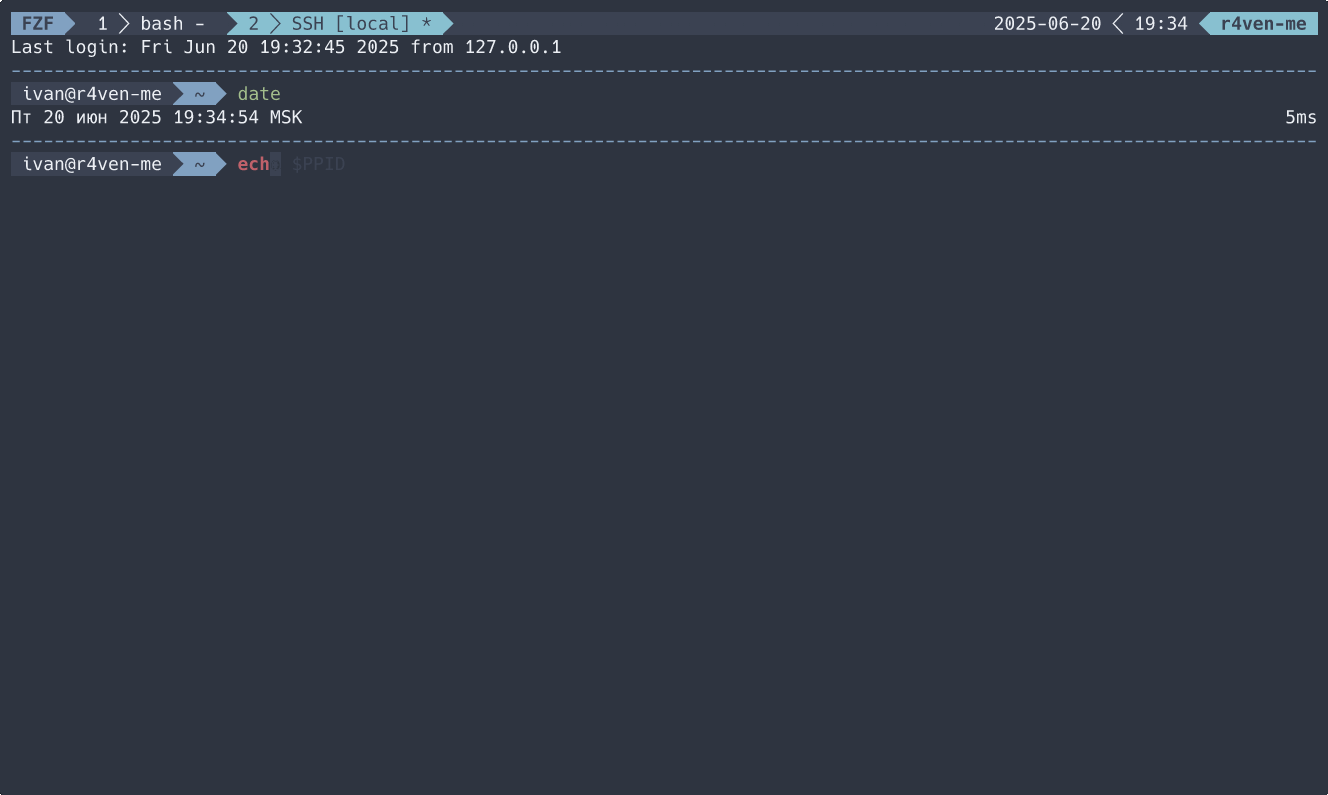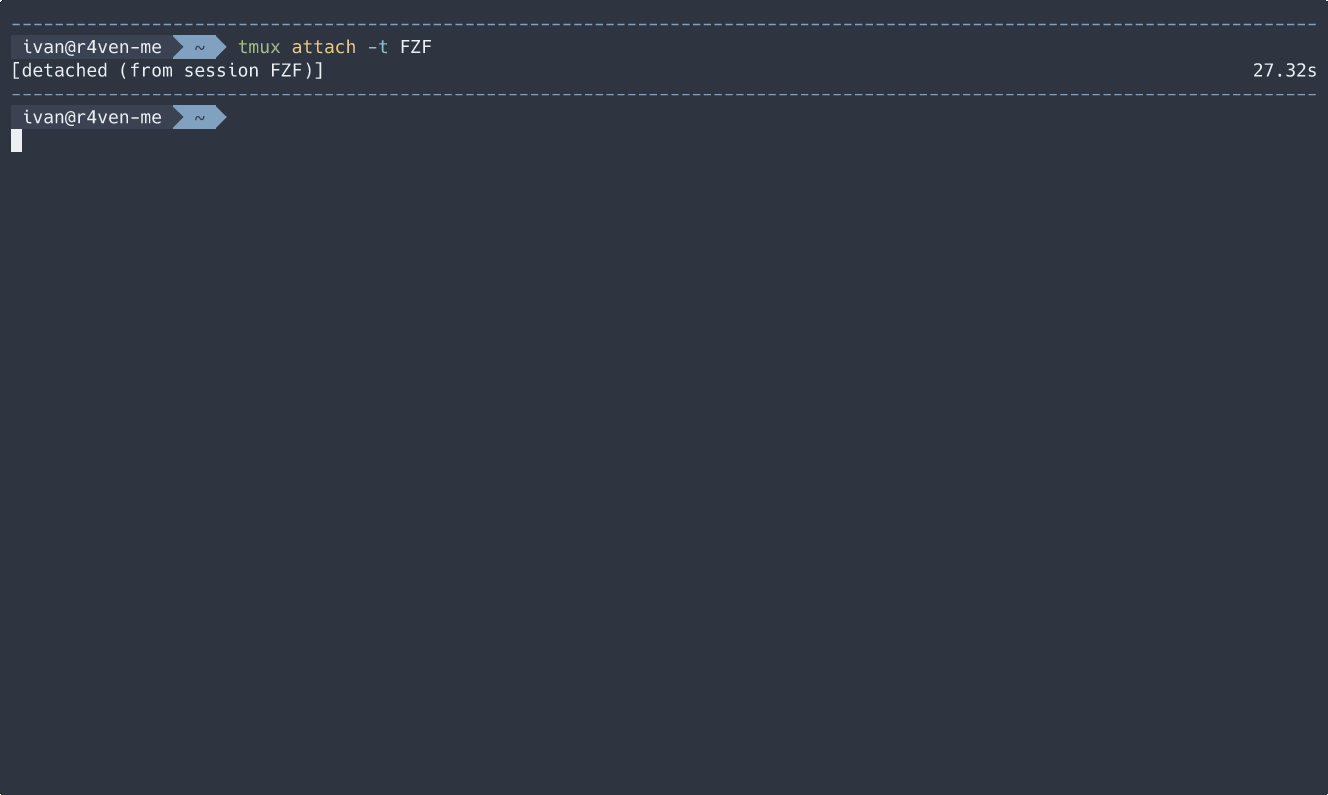
Example of filling in the SSH config
Create/open the SSH client config file with a list of hosts:
nvim ~/.ssh/configFill it in approximately like this:
Host local
    HostName localhost
    User ivan
    Port 22

Host test
   HostName test.r4ven.me
  User ivan
Port 2222We discussed fine-tuning the SSH client in more detail in this article.
Here is the command list itself:
The list below is synchronized with KorTerm and uses the same ten thematic groups.
Parameters appear at the beginning of each line. Replace the examples with your own values before running a command.
Replace VM_ID_HERE and PID_HERE with numeric identifiers.
The templates contain no additional nonempty-parameter checks. The commands retain their original internal conditions.
⚠️ Warning
Do not run the entire collection as a script. These independent examples include deletion and system configuration changes. Example paths do not guarantee safe deletion or overwriting. Check every value before use. Commands without parameters can also perform dangerous actions, including clearing firewall rules or rebooting the system. Run native SQL and guestfish commands inside their respective clients, not in the shell.
System & Diagnostics
  1# ps: top 5 cpu processes
  2# Show the top 5 processes by CPU usage
  3LINES='6'; ps --sort=-%cpu -eo user,pid,ppid,state,comm | head -n "$LINES"
  4
  5# ps: top 5 mem processes
  6# Show the top 5 processes by memory usage
  7LINES='6'; ps --sort=-%mem -eo user,pid,ppid,state,comm | head -n "$LINES"
  8
  9# ps: process tree
 10# Print processes as a tree
 11ps -axf -eo user,pid,ppid,state,comm
 12
 13# ps: zombie parents
 14# Find parent processes of zombies
 15ps -eo user,pid,ppid,state,comm | awk 'NR==1 || $4=="Z"'
 16
 17# ps: parent command
 18# Show the parent process command by PID
 19PARENT='PID_HERE'; ps -o pid,command --ppid "$PARENT"
 20
 21# ps: systemd cgroups
 22# Print the hierarchy of cgroups managed by systemd
 23systemd-cgls
 24
 25# pstree: tree hierarchy
 26# Print the process hierarchy (pstree)
 27pstree -p -t -n -C age
 28
 29# list binaries of user processes
 30# Find unique binary files run by the user
 31for pid in $(ps -u "$USER" -o pid); do exe=$(readlink -f /proc/$pid/exe 2> /dev/null); if [[ -e "$exe" ]]; then echo "$pid:$exe"; fi; done | sort -u -t':' -k2,2
 32
 33# cgroup: show memory max — pid=$(systemctl show <service-name> -…
 34# Show the maximum memory limit for a process/service cgroup
 35SERVICE='example.service'; pid=$(systemctl show "$SERVICE" -p MainPID --value); cgroup_path=$(grep '^0::' "/proc/$pid/cgroup" | cut -d: -f3); cat "/sys/fs/cgroup$cgroup_path/memory.max"
 36
 37# cgroup: show memory max — pid=<PID>; cgroup_path=$(grep '^0::'…
 38# Show the maximum CPU limit for a process cgroup
 39PID='PID_HERE'; cgroup_path=$(grep '^0::' "/proc/$PID/cgroup" | cut -d: -f3); cat "/sys/fs/cgroup$cgroup_path/cpu.max"
 40
 41# ulimit: proc limits
 42# Show resource limits for a process (ulimit)
 43PID='PID_HERE'; cat "/proc/$PID/limits"
 44
 45# fаind processes using files in dir
 46# Find processes using the specified mount point/directory
 47DIR='/opt'; lsof +D "$DIR" 2> /dev/null | awk 'NR > 1 {print $2, $1}' | sort -u | while read pid p_name; do cmd=$(cat "/proc/$pid/cmdline" 2> /dev/null | tr '\0' ' '); echo "PID: $pid, NAME: $p_name, CMD: $cmd"; done
 48
 49# top: batch mode
 50# Get a process snapshot (top in batch mode)
 51ITERATIONS='1'; top -b -n "$ITERATIONS"
 52
 53# vmstat: cpu utilization
 54# Show current CPU usage (vmstat)
 55INTERVAL='1'; SAMPLES='2'; vmstat "$INTERVAL" "$SAMPLES" | tail -1 | awk '{print 100 - $15 "%"}'
 56
 57# df: show mount points >80%
 58# Print mount points with usage >80%
 59PATTERN='^8[0-9]%'; df -h | awk -v pattern="$PATTERN" '$5 ~ pattern {print $6}'
 60
 61# du: show top20 usage — du -h / 2> /dev/null | sort -rh | head -…
 62# Show the top 20 largest files/directories
 63DIR='/'; LIMIT='20'; du -h "$DIR" 2> /dev/null | sort -rh | head -n "$LIMIT"
 64
 65# du: show top20 usage — du -x --block-size=1 / 2> /dev/null | so…
 66# Show the top 20 largest files/directories (with exact IEC sizes)
 67DIR='/'; LIMIT='20'; du -x --block-size=1 "$DIR" 2> /dev/null | sort -rn | head -n "$LIMIT" | numfmt --to=iec
 68
 69# journalctl: disk usage
 70# Show disk space usage by systemd journals
 71journalctl --disk-usage
 72
 73# show open files in dir
 74# Print open files in the specified directory
 75DIR='/opt'; lsof +D "$DIR"
 76
 77# show uptime as unixtime
 78# Show system boot time in unixtime format
 79date -d "$(uptime -s)" +%s
 80
 81# show top 10 bash history
 82# Print the top 10 most frequently used bash commands
 83LIMIT='10'; history | awk '{print $2}' | sort | uniq -c | sort -rn | head -n "$LIMIT"
 84
 85# show swap usage processes
 86# Print the top 10 processes using swap memory
 87LIMIT='10'; for file in /proc/*/status ; do awk '/VmSwap|Name/{printf $2 " " $3}END{ print ""}' $file; done | sort -k 2 -n -r | head -n "$LIMIT"
 88
 89# show swappiness value
 90# Check the current swappiness value
 91cat /proc/sys/vm/swappiness
 92
 93# show OOM scores
 94# Print OOM scores and adjustments for processes
 95printf "PID\tOOM Score\tOOM Adj\tCommand\n"; while read -r pid comm; do [ -f /proc/$pid/oom_score ] && [ $(cat /proc/$pid/oom_score) != 0 ] && printf "%d\t%d\t\t%d\t%s\n" "$pid" "$(cat /proc/$pid/oom_score)" "$(cat /proc/$pid/oom_score_adj)" "$comm"; done < <(ps -e -o pid= -o comm=) | sort -k 2nr
 96
 97# iotop: show iotop
 98# Disk I/O monitoring (iotop)
 99INTERVAL='5'; iotop -o -P -d "$INTERVAL"
100
101# iostat: mon stat of cpu and devs
102# CPU and disk device statistics monitoring (iostat)
103INTERVAL='2'; iostat -x "$INTERVAL"
104
105# sar: load avg
106# Show the system load average (sar)
107INTERVAL='1'; SAMPLES='5'; sar -q "$INTERVAL" "$SAMPLES"
108
109# journalctl: show all reboots
110journalctl --list-boots
111
112# melisai: install
113URL='https://github.com/dmitriimaksimovdevelop/melisai/releases/latest/download/melisai_Linux_x86_64.tar.gz'; DIR='./example/bin'; curl -fsSL "$URL" | sudo tar -xzf - -C "$DIR" melisai && sudo chmod +x "$DIR/melisai"
114
115# melisai: quick
116OUTPUT='./example/report.json'; melisai collect --profile quick -o "$OUTPUT"
117
118# melisai: deep
119OUTPUT='./example/report.json'; melisai collect --profile deep --ai-prompt -o "$OUTPUT"
120
121# melisai: quick health check
122OUTPUT='./example/report.json'; melisai collect --profile quick -o "$OUTPUT"
123
124# melisai: full analysis with ai prompt
125OUTPUT='./example/report.json'; melisai collect --profile standard --ai-prompt -o "$OUTPUT"
126
127# melisai: deep dive focused on disk
128OUTPUT='./example/report.json'; melisai collect --profile deep --focus disk -o "$OUTPUT"
129
130# melisai: profile a specific process
131PID='PID_HERE'; OUTPUT='./example/report.json'; melisai collect --profile standard --pid "$PID" -o "$OUTPUT"
132
133# melisai: profile a container
134CGROUP='/sys/fs/cgroup/system.slice/nginx.service'; OUTPUT='./example/report.json'; melisai collect --profile standard --cgroup "$CGROUP" -o "$OUTPUT"
135
136# melisai: compare before/after a change
137BEFORE='before.json'; AFTER='after.json'; OUTPUT='./example/report.json'; melisai diff "$BEFORE" "$AFTER" -o "$OUTPUT"
138
139# melisai: melisai:
140REPORT='report.json'; jq '.summary.health_score' "$REPORT"
141
142# melisai: all anomalies
143REPORT='report.json'; jq '.summary.anomalies[]' "$REPORT"
144
145# melisai: copy-paste recommendations
146REPORT='report.json'; jq '.summary.recommendations[] | {type, title, commands}' "$REPORT"
147
148# melisai: network sysctls
149REPORT='report.json'; jq '.categories.network[0].data.sysctls' "$REPORT"
150
151# melisai: page reclaim pressure
152REPORT='report.json'; jq '.categories.memory[0].data.reclaim' "$REPORT"
153
154# melisai: numa miss ratio per node
155REPORT='report.json'; jq '.categories.memory[0].data.numa_nodes[] | {node, miss_ratio, cpus}' "$REPORT"
156
157# melisai: top cpu processes
158REPORT='report.json'; jq '.categories.process[0].data.top_by_cpu[:5]' "$REPORT"
159
160# melisai: bcc histogram percentiles
161REPORT='report.json'; jq '.categories.cpu[].histograms[]? | {name, p50, p99, max}' "$REPORT"
162
163# add cron job
164# Add a new job to the current user's crontab
165SCHEDULE='0 3 * * 0'; COMMAND='printf "Example job\n"'; { crontab -l; printf '%s %s\n' "$SCHEDULE" "$COMMAND"; } | crontab -
166
167# system group add
168# Add a new system group
169GROUPID='1995'; GROUP='<GROUP>'; addgroup --system --gid "$GROUPID" "$GROUP"
170
171# system user add
172# Add a new system user (without a password and shell)
173USERID='1997'; GROUP='zabbix'; NAME='<NAME>'; DESCRIPTION='Zabbix monitoring system'; DIR='/home/example-user'; adduser --system --gecos "$DESCRIPTION" --disabled-password --uid "$USERID" --ingroup "$GROUP" --shell /sbin/nologin --home "$DIR" "$NAME"
174
175# systemd: edit unit
176# Edit a systemd unit file (creates an override)
177SERVICE='example.service'; systemctl edit --full --force "$SERVICE"
178
179# systemd: show slice
180# Show properties of a system slice
181SLICE='system.slice'; systemctl show "$SLICE"
182
183# systemd: show unit params
184# Show all parameters and status of a systemd unit
185SERVICE='example.service'; systemctl show "$SERVICE"
186
187# systemd: status check
188# Check whether a systemd unit is active
189SERVICE='cron'; systemctl is-active --quiet "$SERVICE"
190
191# systemd: debug restart
192# Restart a systemd unit with debug logging enabled
193SERVICE='example.service'; sudo SYSTEMD_LOG_LEVEL=debug systemctl restart "$SERVICE"
194
195# systemd: list cgroups
196# Print the hierarchy of cgroups managed by systemd (alternative)
197sudo systemd-cgls
198
199# systemd: show memory limit
200# Show the maximum memory limit for a systemd unit
201SERVICE='example.service'; systemctl show "$SERVICE" -p MemoryMax
202
203# systemd: set limit
204# Set or change the memory limit for a systemd unit
205SERVICE='example.service'; LIMIT='2G'; systemctl set-property "$SERVICE" "MemoryMax=$LIMIT"
206
207# systemd: top
208# Show cgroup resource usage in top style
209INTERVAL='3'; sudo systemd-cgtop -d "$INTERVAL"
210
211# systemd: show user env
212systemctl --user show-environment
213
214# systemd: check mount unit name
215DIR='/path/to/mount'; systemd-escape -p --suffix=mount "$DIR"
216
217# perf: top
218# Monitor CPU performance in real time (perf top)
219perf top
220
221# perf: summary
222# Get summary performance statistics for a program
223PROGRAM='/usr/bin/true'; perf stat "$PROGRAM"
224
225# perf: record execution
226# Record profiling data for program execution
227PROGRAM='/usr/bin/true'; perf record -g "$PROGRAM"
228
229# perf: record running proc
230# Record profiling data for a running process
231PROGRAM='example-program'; perf record -g -p "$(pidof "$PROGRAM")"
232
233# perf: analyze
234# Analyze recorded profiling data (perf report)
235PERF='./perf.data'; perf report "$PERF"
236
237# dd: test write speed
238# Test disk write speed
239FILE='./example/file.txt'; SIZE='1M'; COUNT='1024'; sync; dd if=/dev/zero of="$FILE" bs="$SIZE" count="$COUNT"; sync
240
241# dd: test read spped
242# Test disk read speed (with cache clearing)
243FILE='./example/file.txt'; SIZE='1M'; COUNT='1024'; sysctl -w vm.drop_caches=3 && dd if="$FILE" of=/dev/null bs="$SIZE" count="$COUNT"
244
245# sysrq reboot
246# Force system reboot through SysRq
247echo b > /proc/sysrq-trigger
248
249# sysrq help
250# Print help for Magic SysRq Key
251LOG='/var/log/kern.log'; echo h > /proc/sysrq-trigger; grep 'sysrq: HELP' "$LOG"
252
253# record terminal session
254CAST='demo.cast'; asciinema rec "$CAST"
255
256# convert cast to gif
257CAST='demo.cast'; GIF='./example/session.gif'; THEME='nord'; FONT='Hack Nerd Font Mono'; HEIGHT='1.3'; SIZE='18'; agg "$CAST" "$GIF" --theme "$THEME" --font-family "$FONT" --line-height "$HEIGHT" --font-size "$SIZE"
258
259# strace exec command
260# Trace system calls of the executed command
261PROGRAM='ls'; ARG='-l'; strace -f -e execve "$PROGRAM" "$ARG"
262
263# strace attach pid
264# Attach to a running process and trace its system calls
265PID='PID_HERE'; strace -p "$PID"
266
267# show process env
268# Print environment variables of a running process
269PID='PID_HERE'; sudo cat "/proc/$PID/environ" | xargs -0 -n1
270
271# make cpu online
272# Enable (activate) a specific CPU core
273CPU='CPU_ID_HERE'; echo 1 > "/sys/devices/system/cpu/cpu$CPU/online"
274
275# logging all output
276# Redirect all script output to syslog and a timestamped file
277exec > >(tee >(logger -t $(basename "${BASH_SOURCE[0]}")) | while IFS= read -r line; do echo "$(date +"[%Y-%m-%d %H:%M:%S.%3N]") - $line"; done | tee -a "${BASH_SOURCE[0]%.*}.log") 2>&1
278
279# print term fg colors
280# Show all 256 terminal foreground colors
281for i in {0..255}; do printf "\e[38;5;%sm%03d " "$i" "$i"; (( (i + 1) % 16 == 0 )) && printf "\e[0m\n"; done; printf "\e[0m\n"
282
283# print term bg colors
284# Show all 256 terminal background colors
285for i in {0..255}; do printf "\e[48;5;${i}m %03d \e[0m" $i; [ $((($i+1)%8)) -eq 0 ] && echo; done
286
287# history: only commands
288# Print only commands from bash history (without numbers and date)
289COLUMN='26'; history | cut -c "$COLUMN-"
290
291# fastfetch
292STRUCTURE='Terminal:DateTime:OS:Uptime:Shell:Kernel:Packages:Locale:Bios:Board:CPU:GPU:Memory:Break:Colors:Break:Version'; fastfetch --structure "$STRUCTURE"
293
294# atch: install
295URL='https://github.com/mobydeck/atch/releases/latest/download/atch-linux-amd64.tgz'; DIR='./example/bin'; curl -fsSL "$URL" | sudo tar -xzf - -C "$DIR" atch && sudo chmod +x "$DIR/atch"
296
297# systemd user: set env display
298SCREEN=':0'; systemctl --user set-environment "DISPLAY=$SCREEN"
299
300# dbus: set env display
301SCREEN=':0'; dbus-update-activation-environment --systemd "DISPLAY=$SCREEN" XAUTHORITY
302
303# dpkg: search package by binary path
304PROGRAM='flock'; dpkg -S "$(which "$PROGRAM")"
305
306# zabbix: ping host
307# Check Zabbix agent availability on a host
308HOST='192.168.1.100'; PORT='10050'; zabbix_get -s "$HOST" -p "$PORT" -k agent.ping
309
310# zsh: download .zshrc
311# Download an example .zshrc configuration
312URL='https://raw.githubusercontent.com/r4ven-me/dots/main/.zshrc'; OUTPUT='./example/output.txt'; curl -fsSL "$URL" --output "$OUTPUT"
313
314# ntpq: peer list, stratum, offset, jitter
315SERVER='example.invalid'; ntpq -p "$SERVER"
316
317# ntpq: system variables (sync status, precision, etc.)
318SERVER='example.invalid'; ntpq -c rv "$SERVER"
319
320# ntpdate: query time without changing the local clock
321SERVER='example.invalid'; ntpdate -q "$SERVER"
322
323# chronyd: one-off server check without running the daemon
324# WARNING: chronyd -q sets the system clock; it is not a read-only time query.
325SERVER='example.invalid'; TIMEOUT='5'; chronyd -q "server $SERVER iburst" -t "$TIMEOUT"
326
327# chronyc: add a server to a running chronyd
328SERVER='example.invalid'; chronyc -a "add server $SERVER iburst"
329
330# chronyc: list time sources
331chronyc sources
332
333# ntpq: peer list (local daemon)
334ntpq -p
335
336# chronyc: detailed source list
337chronyc sources -v
338
339# chronyc: sync status
340chronyc tracking
341
342# timedatectl: all time-sync parameters
343timedatectl show-timesync --all
344
345# resolvectl: NTP servers from resolved
346resolvectl status 2>/dev/null | grep -i ntp
347
348# timesyncd: show config
349CONFIG='/etc/systemd/timesyncd.conf'; cat "$CONFIG"Network & HTTP
  1# grep: grep ip
  2# Find IP addresses in a log file (grep)
  3LOG='/var/log/nginx/access.log'; grep -a -E '([0-9]{1,3}\.){3}[0-9]{1,3}' "$LOG"
  4
  5# list listening ports
  6# Show unique listening TCP/UDP ports
  7ss -tuln | awk '{print $5}' | grep -Eo ':[0-9]+$' | sort -t: -k2 -n -u
  8
  9# ping ignore icmp
 10# Temporarily disable responses to ICMP echo requests (ping)
 11echo 1 | sudo tee /proc/sys/net/ipv4/icmp_echo_ignore_all
 12
 13# check port via curl
 14# Check TCP port availability with curl
 15HOST='10.11.12.13'; PORT='1234'; curl -v "telnet://$HOST:$PORT"
 16
 17# check port via echo
 18# Quick TCP port availability check through bash
 19HOST='r4ven.me'; PORT='443'; echo > "/dev/tcp/$HOST/$PORT" && echo "open" || echo "unavailable"
 20
 21# check port via openssl
 22# Check SSL/TLS port availability with openssl
 23HOST='r4ven.me'; PORT='443'; openssl s_client -connect "$HOST:$PORT"
 24
 25# ip: up/down iface
 26# Bring a network interface up/down
 27IFACE='example0'; sudo ip link set dev "$IFACE" down; sudo ip link set dev "$IFACE" up
 28
 29# sysctl: enable forwarding (temp)
 30# Temporarily enable IP packet forwarding (routing)
 31sysctl -w net.ipv4.ip_forward=1 net.ipv6.conf.all.forwarding=1
 32
 33# sysctl: enable forwarding (perm)
 34# Enable IP packet forwarding permanently (through sysctl.d)
 35CONFIG='./example/sysctl.conf'; echo -e 'net.ipv4.ip_forward = 1\nnet.ipv6.conf.all.forwarding = 1' > "$CONFIG" && sysctl -p "$CONFIG"
 36
 37# ping: parallel ping
 38# Run parallel ping for several hosts
 39COUNT='20'; ATTEMPTS='5'; HOST='nftables.r4ven.me'; PREFIX='out'; seq "$COUNT" | xargs -P "$COUNT" -I{} sh -c 'ping -c "$1" "$2" > "$3_$4.log" 2>&1' sh "$ATTEMPTS" "$HOST" "$PREFIX" {}
 40
 41# caps: cmd with some capabilities
 42# Run a command with specific network capabilities
 43PROGRAM='/usr/bin/true'; CAPS='cap_net_raw+ep'; sudo capsh --caps="$CAPS" -- -c 'exec "$1"' sh "$PROGRAM"
 44
 45# capture dst host:port
 46# Capture packets for a specific host and port
 47IFACE='any'; HOST='10.11.12.13'; PORT='443'; tcpdump -i "$IFACE" -nn -q dst host "$HOST" and dst port "$PORT"
 48
 49# capture packets to file
 50# Capture packets and save them to a pcap file
 51IFACE='any'; HOST='10.11.12.13'; OUTPUT='./example/capture.pcap'; sudo tcpdump -nn -i "$IFACE" host "$HOST" -w "$OUTPUT"
 52
 53# capture packets to stdout
 54# Capture packets and output them to a text file
 55IFACE='any'; HOST='10.11.12.13'; OUTPUT='./example/output.txt'; sudo tcpdump -nn -i "$IFACE" host "$HOST" >> "$OUTPUT"
 56
 57# read pcap dump
 58# View the contents of a pcap file
 59PCAP='./tcpdump.pcap'; sudo tcpdump -qns 0 -X -r "$PCAP" | less
 60
 61# dig default — dig r4ven.me +short +answer +identify
 62# Run a DNS query (dig) and show a short answer
 63HOST='r4ven.me'; dig "$HOST" +short +answer +identify
 64
 65# dig default — dig r4ven.me +short +trace
 66# Run a DNS query with delegation tracing
 67HOST='r4ven.me'; dig "$HOST" +short +trace
 68
 69# dig alt ns
 70# Run a DNS query against the specified name server
 71HOST='r4ven.me'; DNS='8.8.8.8'; dig "@$DNS" "$HOST" +short +answer +identify
 72
 73# nmap tcp port check
 74# Check the status of a specific TCP port (nmap)
 75HOST='10.11.12.13'; PORT='22'; nmap "$HOST" -p "$PORT"
 76
 77# nmap udp port check
 78# Check the status of a specific UDP port (nmap)
 79HOST='10.11.12.13'; PORT='53'; nmap -sU "$HOST" -p "$PORT"
 80
 81# quick ports scan
 82HOST='127.0.0.1'; FIRST='1'; LAST='1024'; TIMEOUT='2'; for port in $(seq "$FIRST" "$LAST"); do timeout "$TIMEOUT" bash -c 'echo > "/dev/tcp/$1/$2"' sh "$HOST" "$port" 2>/dev/null && echo "Port $port open"; done
 83
 84# nc: tcp server — PORT=5000; while true; do echo "Listen $PORT T…
 85# Start a simple TCP server (netcat)
 86PORT='PORT_HERE'; while true; do echo "Listen $PORT TCP port..."; nc -l -p "$PORT" | sed 's/.*/You say: &/'; echo -e "TCP-connection closed.\n"; done
 87
 88# nc: tcp server — while true; do nc -l -p 12345 | tee /dev/tty |…
 89# Start a TCP server with a 'pong' response
 90PORT='PORT_HERE'; while true; do nc -l -p "$PORT" | tee /dev/tty | { read line; echo "pong"; } ; done
 91
 92# nc: udp server
 93# Start a simple UDP server (netcat)
 94PORT='PORT_HERE'; while true; do echo "pong" | nc -u -l -p "$PORT"; done
 95
 96# nc: tcp client
 97HOST='127.0.0.1'; PORT='12345'; MESSAGE='hello tcp'; echo "$MESSAGE" | nc -v "$HOST" "$PORT"
 98
 99# nc: udp client
100# Send a message to a UDP server (netcat)
101HOST='127.0.0.1'; PORT='9999'; MESSAGE='ping'; TIMEOUT='1'; echo "$MESSAGE" | nc -u -w "$TIMEOUT" "$HOST" "$PORT"
102
103# socat: udp server
104# Start a UDP server with a 'pong' response (socat)
105PORT='PORT_HERE'; socat -v "UDP-RECVFROM:$PORT,fork" SYSTEM:"echo 'pong'"
106
107# socat: tcp server
108# Start a TCP server with a 'pong' response (socat)
109PORT='PORT_HERE'; socat -v "TCP-LISTEN:$PORT,fork" SYSTEM:"echo 'pong'"
110
111# socat: udp client
112# Send a message to a UDP server (socat)
113HOST='127.0.0.1'; PORT='9999'; MESSAGE='ping'; echo "$MESSAGE" | socat - "UDP:$HOST:$PORT"
114
115# socat: tcp client
116# Send a message to a TCP server (socat)
117HOST='127.0.0.1'; PORT='9999'; MESSAGE='ping'; echo "$MESSAGE" | socat - "TCP:$HOST:$PORT"
118
119# ncat: web page with autorefresh
120# Create a simple auto-refreshing web page (ncat)
121PORT='PORT_HERE'; ncat -lk "$PORT" -c 'echo -e "HTTP/1.1 200 OK\nContent-Type: text/html\n\n<html><meta http-equiv=\"refresh\" content=\"1\"><pre>$(date)\nONLINE</pre></html>"'
122
123# unbound: flush record cashe
124DOMAIN='example.invalid'; unbound-control flush "$DOMAIN"
125
126# curl: download file
127# Download a file by URL using curl
128URL='https://raw.githubusercontent.com/r4ven-me/dots/main/.zshrc'; OUTPUT='./example/output.txt'; curl -fsSL "$URL" -o "$OUTPUT"
129
130# curl: download file with auth
131URL='https://test.r4ven.me/file-url'; NAME='ivan'; PASSWORD='secretpassword'; PREFIX='./example/download'; curl -k -u "$NAME:$PASSWORD" "$URL" -o "${PREFIX}_$(date '+%F').tgz"
132
133# curl: trace request
134# Run an HTTP request with network interaction tracing
135TRACE='./example/trace.txt'; URL='r4ven.me'; curl --trace-ascii "$TRACE" "$URL"
136
137# curl: list all domains
138# Show all hosts curl connected to (including redirects)
139URL='https://example.invalid'; curl -s -L -v "$URL" 2>&1 | grep 'Connected to'
140
141# openwrt: backup
142TARGET='root@openwrt.lan'; ARCHIVE='./example/archive.tar.gz'; ssh "$TARGET" 'sysupgrade --create-backup -' | cat > "$ARCHIVE"
143
144# openwrt: restore
145TARGET='example-user@example.invalid'; ARCHIVE='./example/archive.tar.gz'; cat "$ARCHIVE" | ssh "$TARGET" 'sysupgrade --restore-backup -'
146
147# nc: tcp client with timeout
148# Send a message to a TCP server (netcat)
149HOST='test.r4ven.me'; PORT='12345'; MESSAGE='Hello TCP'; TIMEOUT='1'; echo "$MESSAGE" | timeout "$TIMEOUT" nc -v "$HOST" "$PORT"Firewalls
  1# iptables: track icmp
  2# Start tracking ICMP echo requests (iptables)
  3CHAIN='<CHAIN>'; LIST='PING_LIST'; iptables -A "$CHAIN" -p icmp --icmp-type echo-request -m recent --set --name "$LIST"
  4
  5# iptables: limit icmp
  6# Limit the number of ICMP echo requests (iptables)
  7CHAIN='<CHAIN>'; LIST='PING_LIST'; WINDOW='10'; HITS='5'; iptables -A "$CHAIN" -p icmp --icmp-type echo-request -m recent --update --seconds "$WINDOW" --hitcount "$HITS" --name "$LIST" -j DROP
  8
  9# iptables: order of rules
 10CHAIN='FORWARD'; iptables -L "$CHAIN" -n -v --line-numbers
 11
 12# nftables replace rule
 13# Replace an existing nftables rule by its 'handle' (from the "Network" section)
 14FAMILY='inet'; TABLE='filter'; CHAIN='input'; HANDLE='RULE_HANDLE_HERE'; PORT='2222'; sudo nft replace rule "$FAMILY" "$TABLE" "$CHAIN" handle "$HANDLE" "tcp dport $PORT accept comment \"Allow SSH\""
 15
 16# nftables: show log
 17# View nftables logs in real time (from the "Network" section)
 18PATTERN='NFT-DROP'; sudo journalctl -k -f -g "$PATTERN"
 19
 20# ipset: statistic
 21INTERVAL='1'; watch -n "$INTERVAL" 'ipset -L | grep packets | sort -nrk3 | column -t'
 22
 23# ipset: add rule (accept net)
 24SET='white_list_nets'; NETWORK='192.0.2.0/24'; ipset add "$SET" "$NETWORK" comment "ACCEPT $NETWORK net"
 25
 26# ipset: add rule (accept port)
 27SET='white_list_ports'; HOST='example.invalid'; PROTOCOL='tcp'; PORT='8080'; ipset add "$SET" "$HOST,$PROTOCOL:$PORT" comment "ACCEPT $HOST"
 28
 29# nft: basic rules — flush ruleset
 30# Flush the entire nftables ruleset
 31nft "flush ruleset"
 32
 33# nft: basic rules — add table inet filter
 34# Add the 'filter' table in the 'inet' family
 35FAMILY='inet'; TABLE='<TABLE>'; nft "add table $FAMILY $TABLE"
 36
 37# nft: basic rules — flush table inet filter
 38# Flush all rules in the 'inet filter' table
 39FAMILY='inet'; TABLE='<TABLE>'; nft "flush table $FAMILY $TABLE"
 40
 41# nft: basic rules — add table inet nat
 42# Add the 'nat' table in the 'inet' family
 43FAMILY='inet'; TABLE='<TABLE>'; nft "add table $FAMILY $TABLE"
 44
 45# nft: basic rules — flush table inet nat
 46# Flush all rules in the 'inet nat' table
 47FAMILY='inet'; TABLE='<TABLE>'; nft "flush table $FAMILY $TABLE"
 48
 49# nft: basic rules — add set inet filter lan4 { type ipv4_addr; f…
 50# Create a set for private LAN IPv4 addresses
 51FAMILY='inet'; TABLE='filter'; SET='<SET>'; MEMBERS='10.0.0.0/8, 172.16.0.0/12, 192.168.0.0/16, 169.254.0.0/16'; nft "add set $FAMILY $TABLE $SET { type ipv4_addr; flags interval; elements = { $MEMBERS } }"
 52
 53# nft: basic rules — add set inet filter lan6 { type ipv6_addr; f…
 54# Create a set for private LAN IPv6 addresses
 55FAMILY='inet'; TABLE='filter'; SET='<SET>'; MEMBERS='fd00::/8, fe80::/10'; nft "add set $FAMILY $TABLE $SET { type ipv6_addr; flags interval; elements = { $MEMBERS } }"
 56
 57# nft: basic rules — add set inet filter trusted { type ipv4_addr…
 58# Create a set for trusted IPv4 addresses
 59FAMILY='inet'; TABLE='filter'; SET='<SET>'; MEMBERS='123.34.56.78'; nft "add set $FAMILY $TABLE $SET { type ipv4_addr; elements = { $MEMBERS } }"
 60
 61# nft: basic rules — add chain inet filter input { type filter ho…
 62# Add the 'input' chain with the 'drop' policy
 63FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; PRIORITY='0'; nft "add chain $FAMILY $TABLE $CHAIN { type filter hook input priority $PRIORITY; policy drop; }"
 64
 65# nft: basic rules — add chain inet filter forward { type filter…
 66# Add the 'forward' chain with the 'drop' policy
 67FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; PRIORITY='50'; nft "add chain $FAMILY $TABLE $CHAIN { type filter hook forward priority $PRIORITY; policy drop; }"
 68
 69# nft: basic rules — add chain inet filter output { type filter h…
 70# Add the 'output' chain with the 'accept' policy
 71FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; PRIORITY='-200'; nft "add chain $FAMILY $TABLE $CHAIN { type filter hook output priority $PRIORITY; policy accept; }"
 72
 73# nft: basic rules — add chain inet nat prerouting { type nat hoo…
 74# Add the 'prerouting' chain for NAT
 75FAMILY='inet'; TABLE='nat'; CHAIN='<CHAIN>'; nft "add chain $FAMILY $TABLE $CHAIN { type nat hook prerouting priority dstnat; policy accept; }"
 76
 77# nft: basic rules — add chain inet nat postrouting { type nat ho…
 78# Add the 'postrouting' chain for NAT
 79FAMILY='inet'; TABLE='nat'; CHAIN='<CHAIN>'; nft "add chain $FAMILY $TABLE $CHAIN { type nat hook postrouting priority srcnat; policy accept; }"
 80
 81# nft: basic rules — add chain inet filter input_wan
 82# Add the auxiliary 'input_wan' chain
 83FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add chain $FAMILY $TABLE $CHAIN"
 84
 85# nft: basic rules — add chain inet filter input_lan
 86# Add the auxiliary 'input_lan' chain
 87FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add chain $FAMILY $TABLE $CHAIN"
 88
 89# nft: basic rules — add chain inet filter log_drop
 90# Add a chain for logging dropped packets
 91FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add chain $FAMILY $TABLE $CHAIN"
 92
 93# nft: basic rules — Drop invalid connections
 94# Drop packets with an invalid connection state
 95FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add rule $FAMILY $TABLE $CHAIN ct state invalid drop comment \"Drop invalid connections\""
 96
 97# nft: basic rules — Allow established connections
 98# Allow established and related connections
 99FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add rule $FAMILY $TABLE $CHAIN ct state { established, related } accept comment \"Allow established connections\""
100
101# nft: basic rules — Allow loopback
102# Allow traffic through the loopback interface
103FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add rule $FAMILY $TABLE $CHAIN iif lo accept comment \"Allow loopback\""
104
105# nft: basic rules — Allow trusted IPs
106# Allow incoming traffic from trusted IP addresses
107FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; SET='trusted'; nft "add rule $FAMILY $TABLE $CHAIN ip saddr @$SET accept comment \"Allow trusted IPs\""
108
109# nft: basic rules — ICMP rate limited
110# Limit the ICMP traffic rate
111FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; RATE='10/second'; nft "add rule $FAMILY $TABLE $CHAIN meta l4proto icmp icmp type { echo-request, destination-unreachable, time-exceeded } limit rate $RATE accept comment \"ICMP rate limited\""
112
113# nft: basic rules — Necessary IPv6 ICMP
114# Allow required IPv6 ICMP traffic
115FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add rule $FAMILY $TABLE $CHAIN meta l4proto ipv6-icmp icmpv6 type { destination-unreachable, packet-too-big, time-exceeded, parameter-problem, mld-listener-query, mld-listener-report, mld-listener-reduction, nd-router-solicit, nd-router-advert, nd-neighbor-solicit, nd-neighbor-advert, mld2-listener-report } accept comment \"Necessary IPv6 ICMP\""
116
117# nft: basic rules — Allow UDP traceroute
118# Allow UDP traceroute
119FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; PORT='33434'; nft "add rule $FAMILY $TABLE $CHAIN udp dport $PORT-33534 reject comment \"Allow UDP traceroute\""
120
121# nft: basic rules — LAN IPv4 processing
122# Redirect IPv4 traffic from LAN to the 'input_lan' chain
123FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; SET='lan4'; TARGET='input_lan'; nft "add rule $FAMILY $TABLE $CHAIN ip saddr @$SET jump $TARGET comment \"LAN IPv4 processing\""
124
125# nft: basic rules — LAN IPv6 processing
126# Redirect IPv6 traffic from LAN to the 'input_lan' chain
127FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; SET='lan6'; TARGET='input_lan'; nft "add rule $FAMILY $TABLE $CHAIN ip6 saddr @$SET jump $TARGET comment \"LAN IPv6 processing\""
128
129# nft: basic rules — WAN IPv4 processing
130# Redirect IPv4 traffic from WAN to the 'input_wan' chain
131FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; SET='lan4'; TARGET='input_wan'; nft "add rule $FAMILY $TABLE $CHAIN ip saddr != @$SET jump $TARGET comment \"WAN IPv4 processing\""
132
133# nft: basic rules — WAN IPv6 processing
134# Redirect IPv6 traffic from WAN to the 'input_wan' chain
135FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; SET='lan6'; TARGET='input_wan'; nft "add rule $FAMILY $TABLE $CHAIN ip6 saddr != @$SET jump $TARGET comment \"WAN IPv6 processing\""
136
137# nft: basic rules — Default drop
138# Redirect the remaining incoming traffic to the 'log_drop' chain
139FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; TARGET='log_drop'; nft "add rule $FAMILY $TABLE $CHAIN jump $TARGET comment \"Default drop\""
140
141# nft: basic rules — Allow all TCP/UDP from LAN
142# Allow all TCP/UDP traffic from LAN
143FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add rule $FAMILY $TABLE $CHAIN meta l4proto { tcp, udp } accept comment \"Allow all TCP/UDP from LAN\""
144
145# nft: basic rules — Allowed TCP ports from LAN
146# Allow specific TCP ports from LAN
147FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; PORTS='80, 443'; nft "add rule $FAMILY $TABLE $CHAIN tcp dport { $PORTS } accept comment \"Allowed TCP ports from LAN\""
148
149# nft: basic rules — Allowed UDP ports from LAN
150# Allow specific UDP ports from LAN
151FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; PORTS='53, 123'; nft "add rule $FAMILY $TABLE $CHAIN udp dport { $PORTS } accept comment \"Allowed UDP ports from LAN\""
152
153# nft: basic rules — Drop all from LAN with log
154# Drop new connections from LAN with logging
155FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; TARGET='log_drop'; nft "add rule $FAMILY $TABLE $CHAIN ct state new jump $TARGET comment \"Drop all from LAN with log\""
156
157# nft: basic rules — Allow SSH from WAN
158# Allow SSH from WAN
159FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; PORT='22'; nft "add rule $FAMILY $TABLE $CHAIN tcp dport $PORT accept comment \"Allow SSH from WAN\""
160
161# nft: basic rules — Allowed TCP ports from WAN
162# Allow specific TCP ports from WAN
163FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; PORTS='80, 443'; nft "add rule $FAMILY $TABLE $CHAIN tcp dport { $PORTS } accept comment \"Allowed TCP ports from WAN\""
164
165# nft: basic rules — Allowed UDP ports from WAN
166# Allow specific UDP ports from WAN
167FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; PORTS='53, 123'; nft "add rule $FAMILY $TABLE $CHAIN udp dport { $PORTS } accept comment \"Allowed UDP ports from WAN\""
168
169# nft: basic rules — DNAT: 443->43443
170# Allow DNAT for port 443 on eth0
171FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='eth0'; PORT='443'; nft "add rule $FAMILY $TABLE $CHAIN iifname \"$IFACE\" tcp dport $PORT accept comment \"DNAT: 443->43443\""
172
173# nft: basic rules — DNAT: 443->43443 (2)
174# Allow traffic after DNAT on eth0
175FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='eth0'; PORT='43443'; nft "add rule $FAMILY $TABLE $CHAIN iifname \"$IFACE\" ct status dnat tcp dport $PORT accept comment \"DNAT: 443->43443\""
176
177# nft: basic rules — Drop all from WAN
178# Drop new connections from WAN with logging
179FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; TARGET='log_drop'; nft "add rule $FAMILY $TABLE $CHAIN ct state new jump $TARGET comment \"Drop all from WAN\""
180
181# nft: basic rules — add rule inet filter forward ct state establ…
182# Allow established and related connections for forwarding
183FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add rule $FAMILY $TABLE $CHAIN ct state established,related accept"
184
185# nft: basic rules — Allow K8s forward in
186# Allow incoming forwarding for K8s interfaces (cni)
187FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='cni*'; nft "add rule $FAMILY $TABLE $CHAIN iifname \"$IFACE\" accept comment \"Allow K8s forward in\""
188
189# nft: basic rules — Allow K8s forward out
190# Allow outgoing forwarding for K8s interfaces (cni)
191FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='cni*'; nft "add rule $FAMILY $TABLE $CHAIN oifname \"$IFACE\" accept comment \"Allow K8s forward out\""
192
193# nft: basic rules — Allow K8s forward in (2)
194# Allow incoming forwarding for K8s interfaces (flannel)
195FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='flannel.*'; nft "add rule $FAMILY $TABLE $CHAIN iifname \"$IFACE\" accept comment \"Allow K8s forward in\""
196
197# nft: basic rules — Allow K8s forward out (2)
198# Allow outgoing forwarding for K8s interfaces (flannel)
199FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='flannel.*'; nft "add rule $FAMILY $TABLE $CHAIN oifname \"$IFACE\" accept comment \"Allow K8s forward out\""
200
201# nft: basic rules — Allow K8s forward in (3)
202# Allow incoming forwarding for K8s interfaces (Calico VXLAN)
203FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='vxlan.calico'; nft "add rule $FAMILY $TABLE $CHAIN iifname \"$IFACE\" accept comment \"Allow K8s forward in\""
204
205# nft: basic rules — Allow K8s forward out (3)
206# Allow outgoing forwarding for K8s interfaces (Calico VXLAN)
207FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='vxlan.calico'; nft "add rule $FAMILY $TABLE $CHAIN oifname \"$IFACE\" accept comment \"Allow K8s forward out\""
208
209# nft: basic rules — Allow Docker forward in
210# Allow incoming forwarding for Docker bridges
211FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='br-*'; nft "add rule $FAMILY $TABLE $CHAIN iifname \"$IFACE\" accept comment \"Allow Docker forward in\""
212
213# nft: basic rules — Allow Docker forward out
214# Allow outgoing forwarding for Docker bridges
215FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='br-*'; nft "add rule $FAMILY $TABLE $CHAIN oifname \"$IFACE\" accept comment \"Allow Docker forward out\""
216
217# nft: basic rules — Allow VMs forward in
218# Allow incoming forwarding for KVM/libvirt bridges
219FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='virbr*'; nft "add rule $FAMILY $TABLE $CHAIN iifname \"$IFACE\" accept comment \"Allow VMs forward in\""
220
221# nft: basic rules — Allow VMs forward out
222# Allow outgoing forwarding for KVM/libvirt bridges
223FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='virbr*'; nft "add rule $FAMILY $TABLE $CHAIN oifname \"$IFACE\" accept comment \"Allow VMs forward out\""
224
225# nft: basic rules — Allow OC forward in
226# Allow incoming forwarding for VPN tunnels (OpenVPN/WireGuard)
227FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='tun*'; nft "add rule $FAMILY $TABLE $CHAIN iifname \"$IFACE\" accept comment \"Allow OC forward in\""
228
229# nft: basic rules — Allow OC forward out
230# Allow outgoing forwarding for VPN tunnels (OpenVPN/WireGuard)
231FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='tun*'; nft "add rule $FAMILY $TABLE $CHAIN oifname \"$IFACE\" accept comment \"Allow OC forward out\""
232
233# nft: basic rules — Allow WG forward in
234# Allow incoming forwarding for WireGuard interfaces
235FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='wg*'; nft "add rule $FAMILY $TABLE $CHAIN iifname \"$IFACE\" accept comment \"Allow WG forward in\""
236
237# nft: basic rules — Allow WG forward out
238# Allow outgoing forwarding for WireGuard interfaces
239FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; IFACE='wg*'; nft "add rule $FAMILY $TABLE $CHAIN oifname \"$IFACE\" accept comment \"Allow WG forward out\""
240
241# nft: basic rules — Drop all forward
242# Drop new forwarding connections with logging
243FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; TARGET='log_drop'; nft "add rule $FAMILY $TABLE $CHAIN ct state new jump $TARGET comment \"Drop all forward\""
244
245# nft: basic rules — Drop logging
246# Log dropped packets with rate limiting
247FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; RATE='5/second'; PREFIX='NFT-DROP: '; nft "add rule $FAMILY $TABLE $CHAIN limit rate $RATE log prefix \"$PREFIX\" flags all counter comment \"Drop logging\""
248
249# nft: basic rules — Reject TCP
250# Reject TCP connections with an RST packet
251FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add rule $FAMILY $TABLE $CHAIN meta l4proto tcp reject with tcp reset comment \"Reject TCP\""
252
253# nft: basic rules — Reject UDP
254# Reject UDP packets
255FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add rule $FAMILY $TABLE $CHAIN meta l4proto udp reject comment \"Reject UDP\""
256
257# nft: basic rules — Reject other protocols
258# Reject packets from other protocols with an ICMP message
259FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add rule $FAMILY $TABLE $CHAIN counter reject with icmpx type port-unreachable comment \"Reject other protocols\""
260
261# nft: basic rules — Protection from port scanning
262# Protection against port scanning with rate limiting
263FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; RATE='5/second'; nft "add rule $FAMILY $TABLE $CHAIN pkttype host limit rate $RATE counter reject with icmpx type admin-prohibited comment \"Protection from port scanning\""
264
265# nft: basic rules — Drop all
266# Finally drop all packets in the log_drop chain
267FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; nft "add rule $FAMILY $TABLE $CHAIN drop comment \"Drop all\""
268
269# nft: basic rules — DNAT: 443->43443 (3)
270# Configure DNAT: redirect port 443 to 43443
271FAMILY='inet'; TABLE='nat'; CHAIN='<CHAIN>'; IFACE='eth0'; PORT='443'; TOPORT='43443'; nft "add rule $FAMILY $TABLE $CHAIN iifname \"$IFACE\" tcp dport $PORT redirect to $TOPORT comment \"DNAT: 443->43443\""
272
273# nft: basic rules — DNAT:  443->43443
274# Configure DNAT: redirect port 443 to 43443 (alternative syntax)
275FAMILY='inet'; TABLE='nat'; CHAIN='<CHAIN>'; IFACE='eth0'; PORT='443'; TOPORT='43443'; nft "add rule $FAMILY $TABLE $CHAIN iifname \"$IFACE\" tcp dport $PORT dnat to :$TOPORT comment \"DNAT:  443->43443 \""
276
277# nft: basic rules — SNAT: NAT processing for all
278# Configure SNAT (masquerading) for all outgoing traffic (except loopback)
279FAMILY='inet'; TABLE='nat'; CHAIN='<CHAIN>'; nft "add rule $FAMILY $TABLE $CHAIN oifname != lo masquerade comment \"SNAT: NAT processing for all\""
280
281# nft: basic rules — SNAT: NAT procesing for eth0
282# Configure SNAT (masquerading) for outgoing traffic through eth0
283FAMILY='inet'; TABLE='nat'; CHAIN='<CHAIN>'; IFACE='eth0'; nft "add rule $FAMILY $TABLE $CHAIN oifname \"$IFACE\" masquerade comment \"SNAT: NAT procesing for eth0\""
284
285# nft: basic rules — SNAT: NAT procesing for OC
286# Configure SNAT (masquerading) for outgoing traffic through VPN tunnels
287FAMILY='inet'; TABLE='nat'; CHAIN='<CHAIN>'; IFACE='tun*'; nft "add rule $FAMILY $TABLE $CHAIN oifname \"$IFACE\" masquerade comment \"SNAT: NAT procesing for OC\""
288
289# nft: commands — list ruleset
290# Print the entire nftables ruleset
291nft list ruleset
292
293# nft: commands — list tables
294# Print the list of all nftables tables
295nft list tables
296
297# nft: commands — list table inet filter
298# Print rules from a specific table (inet filter)
299FAMILY='inet'; TABLE='filter'; nft list table "$FAMILY" "$TABLE"
300
301# nft: commands — list chain inet filter input
302# Print rules from a specific chain (inet filter input)
303FAMILY='inet'; TABLE='filter'; CHAIN='input'; nft list chain "$FAMILY" "$TABLE" "$CHAIN"
304
305# nft: commands — -a list ruleset
306# Print the entire ruleset with a 'handle' for each rule
307nft -a list ruleset
308
309# nft: commands — flush ruleset
310# Flush all nftables tables and chains
311nft flush ruleset
312
313# nft: commands — flush table inet filter
314# Flush all rules in the 'inet filter' table
315FAMILY='inet'; TABLE='<TABLE>'; nft flush table "$FAMILY" "$TABLE"
316
317# nft: commands — delete table inet filter
318# Delete the 'inet filter' table
319FAMILY='inet'; TABLE='<TABLE>'; nft delete table "$FAMILY" "$TABLE"
320
321# nft: commands — add rule inet filter input tcp dport 22 accept
322# Add a rule: allow SSH on the input chain
323FAMILY='inet'; TABLE='filter'; CHAIN='<CHAIN>'; PORT='22'; nft add rule "$FAMILY" "$TABLE" "$CHAIN" tcp dport "$PORT" accept
324
325# nft: commands — -a list chain inet filter input
326# Print input chain rules with 'handle'
327FAMILY='inet'; TABLE='filter'; CHAIN='input'; nft -a list chain "$FAMILY" "$TABLE" "$CHAIN"
328
329# nft: commands — delete rule inet filter input handle 15
330# Delete a rule from a chain by its 'handle'
331FAMILY='inet'; TABLE='filter'; CHAIN='input'; HANDLE='RULE_HANDLE_HERE'; nft delete rule "$FAMILY" "$TABLE" "$CHAIN" handle "$HANDLE"
332
333# nft: commands — replace rule inet filter input handle 15 tcp dp…
334# Replace a rule in a chain by its 'handle'
335FAMILY='inet'; TABLE='filter'; CHAIN='input'; HANDLE='RULE_HANDLE_HERE'; PORT='2222'; nft replace rule "$FAMILY" "$TABLE" "$CHAIN" handle "$HANDLE" tcp dport "$PORT" accept
336
337# nft: commands — -f /etc/nftables.conf
338# Load nftables rules from a file
339RULES='./example/rules.nft'; nft -f "$RULES"
340
341# nft: commands — -c -f /etc/nftables.conf
342# Check the syntax of an nftables rules file
343RULES='/etc/nftables.conf'; nft -c -f "$RULES"
344
345# nft: commands — -s list ruleset > /etc/nftables.conf
346# Save the current nftables ruleset to a file
347RULES='./example/rules.nft'; nft -s list ruleset > "$RULES"
348
349# nft: commands — monitor
350# Monitor nftables events in real time
351nft monitor
352
353# nft: commands — monitor trace
354# Trace packet traversal through nftables rules
355nft monitor trace
356
357# nft: commands — --debug=netlink -f myrules.nft
358# Load rules with netlink debug information
359RULES='./example/rules.nft'; nft --debug=netlink -f "$RULES"
360
361# firewalld: active zones
362firewall-cmd --get-active-zones
363
364# firewalld: list all
365firewall-cmd --list-all
366
367# firewalld: rich rules
368firewall-cmd --list-rich-rulesSSH & Security
  1# mkpasswd: get password SHA-512 hash
  2mkpasswd --method=sha-512
  3
  4# openssl: get password SHA-512 hash
  5openssl passwd -6
  6
  7# openssl: generate self-signed certificate
  8KEY='./example/private.key'; CERT='./example/certificate.crt'; SUBJECT='/C=RU/ST=Moscow/L=Moscow/O=IVAN/OU=TEST/CN=test.r4ven.me'; DAYS='7300'; BITS='4096'; sudo openssl req -x509 -nodes -days "$DAYS" -newkey "rsa:$BITS" -keyout "$KEY" -out "$CERT" -subj "$SUBJECT"
  9
 10# openssl: change pass for p12
 11INPUT='old.p12'; OUTPUT='./example/output.txt'; openssl pkcs12 -in "$INPUT" -out "$OUTPUT" -export
 12
 13# encrypt tar with openssl
 14# Encrypt a tar archive with OpenSSL (AES-256-CBC)
 15DIR='/var/log/apt'; OUTPUT='./example/output.txt'; tar -czf - "$DIR" | openssl enc -aes-256-cbc -pbkdf2 -e -out "$OUTPUT"
 16
 17# decrypt file with openssl
 18# Decrypt a file encrypted with OpenSSL
 19INPUT='./logs.tar.gz.enc'; OUTPUT='./example/output.txt'; openssl enc -aes-256-cbc -pbkdf2 -d -in "$INPUT" -out "$OUTPUT"
 20
 21# openssl connect
 22# Check an SSL/TLS connection to a server
 23HOST='r4ven.me'; PORT='443'; openssl s_client -connect "$HOST:$PORT"
 24
 25# openssl show cert remote
 26# Retrieve and display a remote SSL/TLS certificate
 27HOST='r4ven.me'; PORT='443'; openssl s_client -connect "$HOST:$PORT" < /dev/null 2> /dev/null | openssl x509 -text
 28
 29# openssl show cert alt
 30# Retrieve a remote SSL/TLS certificate with ServerName specified
 31HOST='r4ven.me'; PORT='443'; SERVER='r4ven.me'; openssl s_client -connect "$HOST:$PORT" -servername "$SERVER" < /dev/null 2>/dev/null | openssl x509 -text
 32
 33# openssl show local cert
 34# View the contents of a local X.509 certificate
 35CERT='./ca-cert.crt'; openssl x509 -in "$CERT" -text -noout
 36
 37# openssl: self-signed cert
 38# Generate a self-signed SSL/TLS certificate
 39KEY='./example/private.key'; CERT='./example/certificate.crt'; SUBJECT='/C=RU/ST=Moscow/L=Moscow/O=Example/OU=TEST/CN=example.com'; DAYS='7300'; BITS='4096'; openssl req -x509 -nodes -days "$DAYS" -newkey "rsa:$BITS" -keyout "$KEY" -out "$CERT" -subj "$SUBJECT"
 40
 41# openssl: md5 of cert
 42# Get the MD5 hash of the certificate public key modulus
 43CERT='/var/lib/kubelet/pki/kubelet.crt'; openssl x509 -noout -modulus -in "$CERT" | openssl md5
 44
 45# openssl: md5 of key
 46# Get the MD5 hash of the private key modulus
 47KEY='/var/lib/kubelet/pki/kubelet.key'; openssl rsa -noout -modulus -in "$KEY" | openssl md5
 48
 49# mkcert: local tls certs
 50# Create local trusted TLS certificates with mkcert
 51CERT='./example/certificate.crt'; KEY='./example/private.key'; DOMAIN='jenkins.local'; mkcert -cert-file "$CERT" -key-file "$KEY" "$DOMAIN" "localhost" "127.0.0.1"
 52
 53# tls rhel: list tls orgs certs
 54# Print the list of trusted root certificates (RHEL/CentOS)
 55CA='/etc/pki/tls/certs/ca-bundle.crt'; openssl crl2pkcs7 -nocrl -certfile "$CA" | openssl pkcs7 -print_certs -text | grep "Subject:"
 56
 57# tls deb: list tls orgs certs
 58# Print the list of trusted root certificates (Debian/Ubuntu)
 59CA='/etc/ssl/certs/ca-certificates.crt'; openssl crl2pkcs7 -nocrl -certfile "$CA" | openssl pkcs7 -print_certs -text | grep "Subject:"
 60
 61# tls rhel: add new cert
 62# Add a new trusted certificate to the system (RHEL/CentOS)
 63CERT='./example/certificate.crt'; NAME='example-ca'; cp -- "$CERT" "/etc/pki/ca-trust/source/anchors/$NAME.crt" | update-trust extract
 64
 65# tls deb: add new cert
 66# Add a new trusted certificate to the system (Debian/Ubuntu)
 67CERT='./example/certificate.crt'; NAME='example-ca'; cp -- "$CERT" "/usr/local/share/ca-certificates/$NAME.crt" | update-ca-certificates
 68
 69# tls: list orgs
 70# Print the list of trusted organizations from the system store
 71trust list | less
 72
 73# gpg encrypt file
 74# Encrypt a file with a symmetric key using GPG
 75PASSFILE='./example/passphrase.txt'; FILE='./example/file.txt'; gpg --batch --passphrase-file "$PASSFILE" --symmetric --cipher-algo AES256 -- "$FILE"
 76
 77# htpasswd: add user entry to file
 78NAME='<NAME>'; PASSFILE='./example/htpasswd'; sudo sh -c 'printf "%s:" "$1" >> "$2"' sh "$NAME" "$PASSFILE"
 79
 80# htpasswd: generate password hash
 81PASSFILE='./example/htpasswd'; sudo sh -c 'openssl passwd -apr1 >> "$1"' sh "$PASSFILE"
 82
 83# openssl: fetch server public ssl certificate
 84HOST='test.r4ven.me'; PORT='443'; SERVER='test.r4ven.me'; CERT='./example/certificate.crt'; echo | openssl s_client -connect "$HOST:$PORT" -servername "$SERVER" 2> /dev/null | openssl x509 -outform PEM | tee "$CERT"
 85
 86# ca: copy certificate to trusted store
 87CERT='./test.r4ven.me.crt'; DEST='./example/trusted-certificate.crt'; sudo cp -v "$CERT" "$DEST"
 88
 89# ca: update trusted certificates database
 90sudo update-ca-certificates
 91
 92# age: create secret
 93KEY='./example/private.key'; age-keygen --output "$KEY"
 94
 95# age: ecnrypt file
 96ENCRYPTED='./example/file.age'; KEY='./age.key'; FILE='./file.txt'; age --encrypt --identity "$KEY" --output "$ENCRYPTED" "$FILE"
 97
 98# age: ecnrypt file with pubkey
 99RECIPIENT='age1kuheujfd32xdt2uchz3cue303jeeh7cv6lspurnz3fc2xt7chuzsvuh3lf'; ENCRYPTED='./example/file.age'; FILE='./file.txt'; age --encrypt --recipient "$RECIPIENT" --output "$ENCRYPTED" "$FILE"
100
101# age: ecnrypt stdin
102ENCRYPTED='./example/file.age'; KEY='./age.key'; FILE='./file.txt'; tar -cz "$FILE" | age --encrypt --identity "$KEY" > "$ENCRYPTED"
103
104# age: ecnrypt stdin to stdout
105ENCRYPTED='./example/file.age'; KEY='./age.key'; FILE='./file.txt'; tar -cz "$FILE" | age --encrypt --identity "$KEY" --output "$ENCRYPTED"
106
107# age: decrypt file
108ENCRYPTED='./file.txt.age'; KEY='./age.key'; FILE='./example/file.txt'; age --decrypt --identity "$KEY" --output "$FILE" "$ENCRYPTED"
109
110# age: decrypt file to stdout
111ENCRYPTED='./file.tgz.age'; OUTPUT='./example/output.txt'; KEY='./age.key'; age --decrypt --identity "$KEY" "$ENCRYPTED" > "$OUTPUT"
112
113# certbot: get letsencrypt certs
114EMAIL='user@example.invalid'; DOMAIN='example.invalid'; CONFIG='./certbot/conf'; WEBROOT='./certbot/www'; IMAGE='certbot/certbot'; docker run --rm -p 80:80 -v "$CONFIG:/etc/letsencrypt" -v "$WEBROOT:/var/www/certbot" "$IMAGE" -v certonly --non-interactive --standalone --preferred-challenges http --agree-tos --email "$EMAIL" -d "$DOMAIN" --force-renewal
115
116# ssh: create key
117KEY='./example/private.key'; ssh-keygen -t ed25519 -f "$KEY"
118
119# ssh: create key quietly
120# Generate an Ed25519 SSH key without asking for a passphrase
121KEY='./example/private.key'; ssh-keygen -q -N "" -t ed25519 -f "$KEY"
122
123# ssh: change key comment
124# Change the comment of an existing SSH key
125KEY='./example/private.key'; ssh-keygen -c -f "$KEY"
126
127# ssh: show pub key
128# Print the public part of an SSH key from a private file
129KEY="$HOME/.ssh/id_ed25519"; ssh-keygen -y -f "$KEY"
130
131# ssh: copy pub key to remote host
132# Copy a public SSH key to a remote host
133NAME='<NAME>'; HOST='example.invalid'; KEY="$HOME/.ssh/id_ed25519"; ssh-copy-id -i "$KEY" "$NAME@$HOST"
134
135# ssh: port forwarding
136# Configure local SSH port forwarding
137TARGET='example-user@example.invalid'; BIND='127.0.0.1'; LPORT='5432'; RHOST='localhost'; RPORT='5432'; ssh -q -f -N -L "$BIND:$LPORT:$RHOST:$RPORT" "$TARGET"
138
139# ssh: port forwarding temp
140# Configure temporary local SSH port forwarding
141TARGET='example-user@example.invalid'; BIND='127.0.0.1'; LPORT='5432'; RHOST='localhost'; RPORT='5432'; DURATION='60'; ssh -q -f -L "$BIND:$LPORT:$RHOST:$RPORT" "$TARGET" sleep "$DURATION"
142
143# ssh: port forwarding temp full
144# Full temporary local SSH port forwarding with options
145HOST='example.invalid'; PORT='2222'; NAME='ivan'; KEY="$HOME/.ssh/id_ed25519_test"; BIND='127.0.0.1'; LPORT='5432'; RHOST='localhost'; RPORT='5432'; DURATION='60'; ssh -q -f -o StrictHostKeyChecking=no -o UserKnownHostsFile=/dev/null -o ExitOnForwardFailure=yes -L "$BIND:$LPORT:$RHOST:$RPORT" "$HOST" -p "$PORT" -l "$NAME" -i "$KEY" sleep "$DURATION"
146
147# ssh: reverse port forwarding
148# Configure reverse (remote) SSH port forwarding
149TARGET='example-user@example.invalid'; BIND='127.0.0.1'; RPORT='4443'; LHOST='localhost'; LPORT='5001'; ssh -q -f -N -R "$BIND:$RPORT:$LHOST:$LPORT" "$TARGET"
150
151# ssh: remove host from known
152# Delete a host record from the known_hosts file
153KNOWN="$HOME/.ssh/known_hosts"; HOST='example.invalid'; ssh-keygen -f "$KNOWN" -R "$HOST"
154
155# ssh: auth conditions - run script
156KEY='ssh-ed25519 REPLACE_WITH_PUBLIC_KEY'; COMMAND='sudo /opt/hugo/deploy.sh'; FILE='./example/authorized_keys'; escaped_command=$(printf '%s' "$COMMAND" | sed 's/\\/\\\\/g; s/"/\\"/g') && printf 'command="%s",no-port-forwarding,no-X11-forwarding,no-agent-forwarding,no-pty %s\n' "$escaped_command" "$KEY" >> "$FILE"
157
158# ssh: auth conditions - allow tunnelling
159KEY='ssh-ed25519 REPLACE_WITH_PUBLIC_KEY'; FILE='./example/authorized_keys'; printf '%s %s\n' 'permitopen="any",no-pty,no-X11-forwarding,no-agent-forwarding,no-user-rc,command="/usr/bin/tail -f /dev/null"' "$KEY" >> "$FILE"
160
161# ssh: new user with auth conditions
162NAME='<NAME>'; KEY='ssh-ed25519 REPLACE_WITH_PUBLIC_KEY'; DIR='/home/example-user'; useradd -m -d "$DIR" -s /usr/sbin/nologin "$NAME" && mkdir -p "$DIR/.ssh" && chown -R "$NAME:$NAME" "$DIR" && chmod 500 "$DIR/.ssh" && printf 'restrict,port-forwarding %s\n' "$KEY" >> "$DIR/.ssh/authorized_keys" && chown "$NAME:$NAME" "$DIR/.ssh/authorized_keys" && chmod 400 "$DIR/.ssh/authorized_keys"
163
164# generate urandom string
165# Generate a random alphanumeric string 8 characters long
166CHARSET='a-zA-Z0-9'; LENGTH='8'; cat /dev/urandom | tr -dc "$CHARSET" | fold -w "$LENGTH" | head -n 1
167
168# vt-cli: check file by url
169URL='https://example.invalid/example-file'; vt scan file <(curl -Ls "$URL") --waitFiles & Sync
  1# list lv and snapshots
  2# Print information about LVM logical volumes and snapshots
  3lvs --options lv_name,lv_size,origin,lv_attr
  4
  5# sed: replace text
  6# Replace text in a file (creating a backup copy)
  7FILE='./example/file.txt'; EXPR='s/old_text/new_text/g'; sed -i.bkp "$EXPR" -- "$FILE"
  8
  9# sed: insert first line
 10# Insert a new line at the beginning of a file
 11FILE='./example/file.txt'; EXPR='1i test_line'; sed -i.bkp "$EXPR" -- "$FILE"
 12
 13# sed: insert first block
 14# Insert a multiline block at the beginning of a file
 15FILE='./example/file.txt'; EXPR='1i test_line:\n    value1\n    value2'; sed -i.bkp "$EXPR" -- "$FILE"
 16
 17# sed: change substring
 18# Change a substring in a line that starts with a specific pattern
 19EXPR='\|^test_line|s|line|word|'; sed "$EXPR"
 20
 21# find: chmod files
 22# Find and set permissions 644 for all files
 23DIR='./example/directory'; MODE='644'; find "$DIR" -type f -exec chmod "$MODE" {} \;
 24
 25# find: chmod dirs
 26# Find and set permissions 755 for all directories
 27DIR='./example/directory'; MODE='755'; find "$DIR" -type d -exec chmod "$MODE" {} \;
 28
 29# find: exclude path
 30# Search for files while excluding specific paths
 31DIR='./'; EXCLUDE='./example-excluded'; FILE='example.txt'; find "$DIR" -path "$EXCLUDE" -prune -o -name "$FILE" -ls
 32
 33# find: grep
 34DIR='./'; PATTERN='example'; find "$DIR" -xdev -type f -exec grep -sIrilE "$PATTERN" {} \;
 35
 36# find: du
 37DIR='/'; LIMIT='20'; find "$DIR" -type f -exec du -Sh {} + 2> /dev/null | sort -rh | head -n "$LIMIT"
 38
 39# find: all symlinks
 40# Resolve a chain of symbolic links to the final file
 41LINK='./example-link'; current="$LINK"; while [[ -L "$current" ]]; do target=$(readlink "$current"); echo "$current -> $target"; if [[ "$target" == /* ]]; then current="$target"; else current="$(dirname "$current")/$target"; fi; done; echo "Final: $current"
 42
 43# acl: set rwx access current
 44DIR='./example/directory'; setfacl -R -m m::rwx "$DIR"
 45
 46# acl: set rwx access default
 47DIR='./example/directory'; setfacl -R -m d:m::rwx "$DIR"
 48
 49# acl: set rwX access current
 50DIR='./example/directory'; NAME='<NAME>'; setfacl -R -m u:"$NAME":rwX "$DIR"
 51
 52# acl: set rwX access default
 53DIR='./example/directory'; NAME='<NAME>'; setfacl -R -m d:u:"$NAME":rwX "$DIR"
 54
 55# acl: set full access
 56OWNER='example-user'; DIR='./example/directory'; setfacl -R -m m::rwx "$DIR" && setfacl -R -m d:m::rwx "$DIR" && setfacl -R -m u:"$OWNER":rwX "$DIR" && setfacl -R -m d:u:"$OWNER":rwX "$DIR"
 57
 58# dd: create files with data — dd if=/dev/urandom of=./file1 bs=5…
 59# Create a file with random data
 60OUTPUT='./example/data.bin'; SIZE='50K'; COUNT='10'; dd if=/dev/urandom of="$OUTPUT" bs="$SIZE" count="$COUNT"
 61
 62# dd: create files with data — dd if=/dev/urandom of=./file2 bs=5…
 63# Create a second file with random data
 64OUTPUT='./example/data.bin'; SIZE='50K'; COUNT='10'; dd if=/dev/urandom of="$OUTPUT" bs="$SIZE" count="$COUNT"
 65
 66# lsof: find deleted files
 67# Find open files that were deleted (but are still in use)
 68lsof | grep '(deleted)'
 69
 70# truncate: truncate deleted files
 71# Truncate (clear) the contents of a deleted but open file
 72PID='PID_HERE'; FD='FD_HERE'; truncate -s 0 -- "/proc/$PID/fd/$FD"
 73
 74# ssh: rsync
 75# Synchronize files and directories over SSH using rsync
 76DIR='./example/source'; HOST='example.invalid'; REMOTE='/example/destination'; COMMAND='ssh -q -o StrictHostKeyChecking=no -o UserKnownHostsFile=/dev/null -p 2222 -l test'; rsync --archive --compress --links --hard-links --xattrs --human-readable --protect-args --delete -e "$COMMAND" -- "$DIR" "$HOST:$REMOTE/"
 77
 78# diff: compare two stdouts
 79FILE='./example.txt'; GLOB='*.txt'; PATTERN='example'; diff -y <(cat -- "$FILE") <(find ./ -name "$GLOB" -exec grep -Hni -- "$PATTERN" {} \;)
 80
 81# grep: no comment and empty line
 82CONFIG='/etc/service.conf'; grep -vE '^\s*(#|$)' "$CONFIG"
 83
 84# rclone: copy files
 85SOURCE='./example-source'; DEST='./example/destination'; rclone copy "$SOURCE" "$DEST"
 86
 87# rclone: mirror source to destination (delete extra files)
 88SOURCE='./example/source'; DEST='./example/destination'; rclone sync "$SOURCE" "$DEST"
 89
 90# rclone: move files (copy and delete)
 91SOURCE='./example/source'; DEST='./example/destination'; rclone move "$SOURCE" "$DEST"
 92
 93# rclone: list files
 94REMOTE='example_remote'; rclone ls "$REMOTE:"
 95
 96# rclone: list directories only
 97REMOTE='example_remote'; rclone lsd "$REMOTE:"
 98
 99# rclone: show directory tree
100REMOTE='example_remote'; rclone tree "$REMOTE:"
101
102# rclone: show total size and file count
103REMOTE='example_remote'; rclone size "$REMOTE:"
104
105# rclone: delete files matching filters
106REMOTE='example_remote:example/path'; rclone delete "$REMOTE"
107
108# rclone: delete directory including root
109REMOTE='example_remote:example/path'; rclone purge "$REMOTE"
110
111# rclone: check differences between src and dst
112SOURCE='./example-source'; DEST='./example-destination'; rclone check "$SOURCE" "$DEST"
113
114# rclone: dry-run without making changes
115SOURCE='./example-source'; DEST='./example-destination'; rclone copy "$SOURCE" "$DEST" --dry-run
116
117# rclone: mount remote as filesystem
118REMOTE='example_remote'; MOUNT='./example/mount'; rclone mount "$REMOTE:" "$MOUNT"
119
120# rclone: serve files over HTTP
121REMOTE='example_remote'; rclone serve http "$REMOTE:"
122
123# rclone: serve WebDAV endpoint
124REMOTE='example_remote'; rclone serve webdav "$REMOTE:"
125
126# rclone: configure remotes interactively
127rclone config
128
129# rclone: show configured remotes
130rclone listremotes
131
132# rclone: copy using checksum verification
133SOURCE='./example-source'; DEST='./example/destination'; rclone copy "$SOURCE" "$DEST" --checksum
134
135# rclone: limit bandwidth usage
136SOURCE='./example-source'; DEST='./example/destination'; BWLIMIT='10M'; rclone copy "$SOURCE" "$DEST" --bwlimit "$BWLIMIT"
137
138# rclone: exclude files by pattern
139SOURCE='./example-source'; DEST='./example/destination'; EXCLUDE='*.tmp'; rclone copy "$SOURCE" "$DEST" --exclude "$EXCLUDE"
140
141# rclone: include files by pattern
142SOURCE='./example-source'; DEST='./example/destination'; INCLUDE='*.sql'; rclone copy "$SOURCE" "$DEST" --include "$INCLUDE"
143
144# rclone: show progress during transfer
145SOURCE='./example-source'; DEST='./example/destination'; rclone copy "$SOURCE" "$DEST" --progress
146
147# rclone: increase parallel transfers
148SOURCE='./example-source'; DEST='./example/destination'; TRANSFERS='8'; rclone copy "$SOURCE" "$DEST" --transfers "$TRANSFERS"
149
150# rclone: compare directories without transfer
151SOURCE='./example-source'; DEST='./example-destination'; rclone check "$SOURCE" "$DEST" --one-way
152
153# rclone: generate file hashes list
154REMOTE='example_remote:example-path'; HASH='MD5'; rclone hashsum "$HASH" "$REMOTE"
155
156# rclone: interactive rclone config
157rclone config
158
159# rclone: obscure password
160PASSWORD='example-password'; rclone obscure "$PASSWORD"
161
162# rclone: mount storage
163REMOTE='storage:/data'; MOUNT='./example/mount'; rclone mount --daemon "$REMOTE" "$MOUNT"
164
165# rclone: mount SFTP with options
166REMOTE='example_remote:example/path'; MOUNT='./example/mount'; DIRCACHE='48h'; CACHEMODE='full'; CACHESIZE='10G'; CACHEAGE='24h'; WRITEBACK='5s'; CHUNK='128M'; CHUNKMAX='1G'; BUFFER='128M'; TRANSFERS='8'; CHECKERS='8'; UMASK='002'; LEVEL='INFO'; RETRIES='10'; LOWRETRIES='10'; MODTIME='false'; rclone mount --daemon --allow-other "$REMOTE" "$MOUNT" --dir-cache-time "$DIRCACHE" --vfs-cache-mode "$CACHEMODE" --vfs-cache-max-size "$CACHESIZE" --vfs-cache-max-age "$CACHEAGE" --vfs-write-back "$WRITEBACK" --vfs-read-chunk-size "$CHUNK" --vfs-read-chunk-size-limit "$CHUNKMAX" --buffer-size "$BUFFER" --transfers "$TRANSFERS" --checkers "$CHECKERS" --umask "$UMASK" --log-level "$LEVEL" --retries "$RETRIES" --low-level-retries "$LOWRETRIES" --sftp-set-modtime="$MODTIME" --sftp-disable-hashcheck
167
168# rclone: mount WebDAV with options
169REMOTE='webdav-storage:/data'; MOUNT='./example/mount'; DIRCACHE='48h'; CACHEMODE='full'; CACHESIZE='10G'; CACHEAGE='24h'; WRITEBACK='5s'; CHUNK='128M'; CHUNKMAX='1G'; BUFFER='128M'; TRANSFERS='8'; CHECKERS='8'; UMASK='002'; LEVEL='INFO'; RETRIES='10'; LOWRETRIES='10'; rclone mount --daemon "$REMOTE" "$MOUNT" --dir-cache-time "$DIRCACHE" --vfs-cache-mode "$CACHEMODE" --vfs-cache-max-size "$CACHESIZE" --vfs-cache-max-age "$CACHEAGE" --vfs-write-back "$WRITEBACK" --vfs-read-chunk-size "$CHUNK" --vfs-read-chunk-size-limit "$CHUNKMAX" --buffer-size "$BUFFER" --transfers "$TRANSFERS" --checkers "$CHECKERS" --umask "$UMASK" --log-level "$LEVEL" --retries "$RETRIES" --low-level-retries "$LOWRETRIES"
170
171# rclone: mount S3 with options
172REMOTE='s3-storage:/data'; MOUNT='./example/mount'; DIRCACHE='48h'; CACHEMODE='full'; CACHESIZE='10G'; CACHEAGE='24h'; WRITEBACK='5s'; CHUNK='128M'; CHUNKMAX='1G'; BUFFER='128M'; TRANSFERS='8'; CHECKERS='8'; UMASK='002'; LEVEL='INFO'; RETRIES='10'; LOWRETRIES='10'; POLL='10m'; rclone mount --daemon "$REMOTE" "$MOUNT" --dir-cache-time "$DIRCACHE" --vfs-cache-mode "$CACHEMODE" --vfs-cache-max-size "$CACHESIZE" --vfs-cache-max-age "$CACHEAGE" --vfs-write-back "$WRITEBACK" --vfs-read-chunk-size "$CHUNK" --vfs-read-chunk-size-limit "$CHUNKMAX" --buffer-size "$BUFFER" --transfers "$TRANSFERS" --checkers "$CHECKERS" --umask "$UMASK" --log-level "$LEVEL" --retries "$RETRIES" --low-level-retries "$LOWRETRIES" --poll-interval "$POLL" --s3-chunk-size 64M --s3-upload-cutoff 64M
173
174# rclone: unmount storage
175MOUNT='./example/mount'; fusermount -u "$MOUNT"
176
177# acl: set rwx user access (non-recursive)
178# Set ACL (Access Control List) permissions for a user
179DIR='./example/directory'; NAME='<NAME>'; setfacl -m "u:$NAME:rwx" "$DIR"Archives & Compression
  1# tar: create archive
  2# Create a tar archive from files and directories
  3ARCHIVE='./example/archive.tar'; FILE1='./file1'; FILE2='./file2'; DIR='./dir/'; tar -c -f "$ARCHIVE" "$FILE1" "$FILE2" "$DIR"
  4
  5# tar: create archive with verbose output
  6# Create a tar archive with verbose output
  7ARCHIVE='./example/archive.tar'; FILE1='./file1'; FILE2='./file2'; DIR='./dir/'; tar -v -c -f "$ARCHIVE" "$FILE1" "$FILE2" "$DIR"
  8
  9# tar: create from different directory
 10# Create a tar archive while located in another directory
 11ARCHIVE='./example/archive.tar'; DIR='/tmp/dir/'; tar -C "$DIR" -c -f "$ARCHIVE" ./
 12
 13# tar: extract archive
 14# Extract the contents of a tar archive
 15ARCHIVE='./example/archive.tar'; tar -x -f "$ARCHIVE"
 16
 17# tar: extract to specific directory
 18# Extract a tar archive into the specified directory
 19ARCHIVE='./archive.tar'; DIR='./example/directory'; tar -C "$DIR" -x -f "$ARCHIVE"
 20
 21# tar: list archive contents
 22# Show the list of files in a tar archive
 23ARCHIVE='./archive.tar'; tar -t -f "$ARCHIVE"
 24
 25# tar: verify archive integrity
 26# Check tar archive integrity
 27ARCHIVE='./archive.tar'; tar -t -f "$ARCHIVE" &> /dev/null
 28
 29# tar: add file to archive
 30# Add a file to an existing tar archive
 31ARCHIVE='./example/archive.tar'; FILE='/etc/passwd'; tar -r -f "$ARCHIVE" "$FILE"
 32
 33# tar: delete file from archive
 34# Delete a file from a tar archive
 35ARCHIVE='./example/archive.tar'; MEMBER='example/file.txt'; tar --delete -f "$ARCHIVE" "$MEMBER"
 36
 37# tar: gzip compression
 38# Create a compressed gzip tar archive (.tgz or .tar.gz)
 39ARCHIVE='./example/archive.tar.gz'; FILE1='./file1'; FILE2='./file2'; tar -c -z -f "$ARCHIVE" "$FILE1" "$FILE2"
 40
 41# tar: bzip2 compression
 42# Create a compressed bzip2 tar archive (.tar.bz2)
 43ARCHIVE='./example/archive.tar.bz2'; FILE1='./file1.txt'; FILE2='./file2.txt'; tar -c -j -f "$ARCHIVE" "$FILE1" "$FILE2"
 44
 45# tar: xz compression
 46# Create a compressed xz tar archive (.tar.xz)
 47ARCHIVE='./example/archive.tar.xz'; FILE1='./file1.txt'; FILE2='./file2.txt'; tar -c -J -f "$ARCHIVE" "$FILE1" "$FILE2"
 48
 49# tar: zstd compression
 50# Create a compressed zstd tar archive (.tar.zst)
 51ARCHIVE='./example/archive.tar.zst'; FILE1='./file1.txt'; FILE2='./file2.txt'; tar -c --zstd -f "$ARCHIVE" "$FILE1" "$FILE2"
 52
 53# tar: compression with custom utility
 54# Create an archive specifying an external compression utility
 55ARCHIVE='./example/archive.tar.zst'; FILE1='./file1.txt'; DIR='./dir'; COMPRESSOR='zstd -19'; tar -v -I "$COMPRESSOR" -c -f "$ARCHIVE" "$FILE1" "$DIR"
 56
 57# tar: create archive to stdout
 58# Create a tar archive and send it to stdout
 59ARCHIVE='./example/archive.tar'; FILE1='./file1'; FILE2='./file2'; DIR='./dir/'; tar -c -f - "$FILE1" "$FILE2" "$DIR" > "$ARCHIVE"
 60
 61# tar: create compressed archive to stdout
 62# Create a compressed gzip tar archive and send it to stdout
 63ARCHIVE='./example/archive.tar.gz'; FILE1='./file1'; FILE2='./file2'; DIR='./dir/'; tar -c -z -f - "$FILE1" "$FILE2" "$DIR" > "$ARCHIVE"
 64
 65# tar: pipe to external compressor
 66# Archive and compress data using an external utility (gzip)
 67ARCHIVE='./example/archive.tar'; FILE1='./file1'; FILE2='./file2'; DIR='./dir/'; tar -c -f - "$FILE1" "$FILE2" "$DIR" | gzip -9 > "$ARCHIVE"
 68
 69# tar: archive files found by find
 70# Archive files found by the find command
 71ARCHIVE='./example/archive.tar'; DIR='./'; GLOB='file[1-2]'; find "$DIR" -name "$GLOB" | tar -c -z -f "$ARCHIVE" -T -
 72
 73# tar: send archive to remote host
 74# Archive, compress, and send files to a remote host for extraction
 75DIR='./dir/'; TARGET='example-user@example.invalid'; COMMAND='tar -C /tmp -x -z -f -'; tar -c -z -f - "$DIR" | ssh "$TARGET" "$COMMAND"
 76
 77# tar: create archive on remote host
 78# Create a compressed tar archive on a remote host and download it locally
 79TARGET='ivan@test.r4ven.me'; COMMAND='tar -c -z -f - ./file1 ./file2'; ARCHIVE='./example/archive.tar.gz'; ssh "$TARGET" "$COMMAND" > "$ARCHIVE"
 80
 81# tar: extract remote archive locally
 82# Download and extract a compressed tar archive from a remote host locally
 83TARGET='ivan@test.r4ven.me'; COMMAND='cat ./archive.tgz'; DEST='./example/destination'; ssh "$TARGET" "$COMMAND" | tar -C "$DEST" -x -z -f -
 84
 85# tar: create encrypted archive
 86# Create a compressed and encrypted GPG archive
 87PASSPHRASE='REPLACE_WITH_PASSPHRASE'; ARCHIVE='./example/archive.tar.gz.gpg'; FILE1='./file1'; FILE2='./file2'; DIR='./dir/'; tar -c -z -f - "$FILE1" "$FILE2" "$DIR" | gpg --batch --symmetric --passphrase "$PASSPHRASE" > "$ARCHIVE"
 88
 89# gpg: decrypt and extract archive
 90# Decrypt a GPG archive and extract its contents
 91ARCHIVE='./example/archive.tar.gz.gpg'; gpg -d "$ARCHIVE" | tar -x -z -f -
 92
 93# tar: split archive into parts
 94# Split a compressed tar archive into smaller parts
 95PREFIX='./example/archive.tar.gz.part-'; DIR='./dir/'; SIZE='200K'; tar -c -z -f - "$DIR" | split -b "$SIZE" - "$PREFIX"
 96
 97# cat: combine split archives
 98# Combine split archive parts and extract it
 99PREFIX='./example/archive.tar.gz.part-'; cat "$PREFIX"* | tar -x -z -f -
100
101# gzip: compress file
102# Compress a file with gzip
103FILE1='./example/file.txt'; gzip "$FILE1"
104
105# gzip: decompress file — gunzip ./file1.txt.gz
106# Decompress a gzip archive
107FILE='./example/file.txt'; gunzip "$FILE"
108
109# gzip: decompress file — gzip -d ./file1.txt.gz
110# Decompress a gzip archive (alternative)
111FILE='./example/file.txt'; gzip -d "$FILE"
112
113# gzip: compress keeping original
114# Compress a file while keeping the original
115FILE1='./example/file.txt'; gzip -k "$FILE1"
116
117# gzip: maximum compression
118# Compress a file with the maximum gzip compression level
119FILE1='./example/file.txt'; gzip -9 "$FILE1"
120
121# bzip2: compress file
122# Compress a file with bzip2
123FILE1='./example/file.txt'; bzip2 "$FILE1"
124
125# bzip2: decompress file — bunzip2 ./file1.txt.bz2
126# Decompress a bzip2 archive
127FILE='./example/file.txt'; bunzip2 "$FILE"
128
129# bzip2: decompress file — bzip2 -d ./file1.txt.bz2
130# Decompress a bzip2 archive (alternative)
131FILE='./example/file.txt'; bzip2 -d "$FILE"
132
133# bzip2: compress keeping original
134# Compress a file with bzip2 while keeping the original
135FILE1='./example/file.txt'; bzip2 -k "$FILE1"
136
137# bzip2: maximum compression
138# Compress a file with the maximum bzip2 compression level
139FILE1='./example/file.txt'; bzip2 -9 "$FILE1"
140
141# xz: compress file
142# Compress a file with xz
143FILE1='./example/file.txt'; xz "$FILE1"
144
145# xz: decompress file — unxz ./file1.txt.xz
146# Decompress an xz archive
147FILE='./example/file.txt'; unxz "$FILE"
148
149# xz: decompress file — xz -d ./file1.txt.xz
150# Decompress an xz archive (alternative)
151FILE='./example/file.txt'; xz -d "$FILE"
152
153# xz: compress keeping original
154# Compress a file with xz while keeping the original
155FILE1='./example/file.txt'; xz -k "$FILE1"
156
157# xz: maximum compression
158# Compress a file with the maximum xz compression level
159FILE1='./example/file.txt'; xz -9 "$FILE1"
160
161# zstd: compress file
162# Compress a file with zstd
163FILE1='./example/file.txt'; zstd "$FILE1"
164
165# zstd: compress keeping original
166# Compress a file with zstd while keeping the original
167FILE1='./example/file.txt'; zstd -k "$FILE1"
168
169# zstd: decompress file — unzstd ./file1.txt.zst
170# Decompress a zstd archive
171FILE='./example/file.txt'; unzstd "$FILE"
172
173# zstd: decompress file — zstd -d ./file1.txt.zst
174# Decompress a zstd archive (alternative)
175FILE='./example/file.txt'; zstd -d "$FILE"
176
177# zstd: maximum compression
178# Compress a file with the maximum zstd compression level
179FILE1='./example/file.txt'; zstd -19 "$FILE1"
180
181# zip: create archive
182# Create a ZIP archive from files and directories
183ARCHIVE='./example/archive.zip'; FILE1='./file1'; DIR='./dir/'; zip "$ARCHIVE" "$FILE1" "$DIR"
184
185# unzip: extract archive
186# Extract the contents of a ZIP archive
187ARCHIVE='./example/archive.zip'; unzip "$ARCHIVE"
188
189# unzip: list archive contents
190# Show the list of files in a ZIP archive
191ARCHIVE='./archive.zip'; unzip -l "$ARCHIVE"
192
193# zip: add file to archive
194# Add a file to an existing ZIP archive
195ARCHIVE='./example/archive.zip'; FILE2='./file2'; zip "$ARCHIVE" "$FILE2"
196
197# zip: no compression
198# Create a ZIP archive without compression
199ARCHIVE='./example/archive.zip'; FILE1='./file1.txt'; zip -0 "$ARCHIVE" "$FILE1"
200
201# zip: maximum compression
202# Create a ZIP archive with maximum compression
203ARCHIVE='./example/archive.zip'; FILE1='./file1.txt'; zip -9 "$ARCHIVE" "$FILE1"
204
205# 7z: create archive
206# Create a 7z archive from files and directories
207ARCHIVE='./example/archive.7z'; FILE1='./file1'; DIR='./dir/'; 7z a "$ARCHIVE" "$FILE1" "$DIR"
208
209# 7z: extract archive
210# Extract the contents of a 7z archive
211ARCHIVE='./example/archive.7z'; 7z x "$ARCHIVE"
212
213# 7z: list archive contents
214# Show the list of files in a 7z archive
215ARCHIVE='./archive.7z'; 7z l "$ARCHIVE"
216
217# 7z: add file to archive
218# Add a file to an existing 7z archive
219ARCHIVE='./example/archive.7z'; FILE2='./file2'; 7z a "$ARCHIVE" "$FILE2"
220
221# 7z: no compression
222# Create a 7z archive without compression
223ARCHIVE='./example/archive.7z'; FILE1='./file1.txt'; 7z a -mx=0 "$ARCHIVE" "$FILE1"
224
225# 7z: maximum compression
226# Create a 7z archive with maximum compression
227ARCHIVE='./example/archive.7z'; FILE1='./file1.txt'; 7z a -mx=9 "$ARCHIVE" "$FILE1"
228
229# rar: create archive
230# Create a RAR archive from files and directories
231ARCHIVE='./example/archive.rar'; FILE1='./file1'; DIR='./dir/'; rar a "$ARCHIVE" "$FILE1" "$DIR"
232
233# unrar: extract archive
234# Extract the contents of a RAR archive
235ARCHIVE='./example/archive.rar'; unrar x "$ARCHIVE"
236
237# unrar: list archive contents
238# Show the list of files in a RAR archive
239ARCHIVE='./archive.rar'; unrar l "$ARCHIVE"
240
241# rar: add file to archive
242# Add a file to an existing RAR archive
243ARCHIVE='./example/archive.rar'; FILE2='./file2'; rar a "$ARCHIVE" "$FILE2"
244
245# rar: no compression
246# Create a RAR archive without compression
247ARCHIVE='./example/archive.rar'; FILE1='file1.txt'; rar a -m0 "$ARCHIVE" "$FILE1"
248
249# rar: maximum compression
250# Create a RAR archive with maximum compression
251ARCHIVE='./example/archive.rar'; FILE1='file1.txt'; rar a -m5 "$ARCHIVE" "$FILE1"
252
253# zip: create test archive
254# Create a ZIP archive for testing
255ARCHIVE='./example/archive.zip'; PREFIX='./file'; DIR='./dir'; zip -9 "$ARCHIVE" "$PREFIX"* "$DIR"
256
257# 7z: create test archive
258# Create a 7z archive for testing
259ARCHIVE='./example/archive.7z'; PREFIX='./file'; DIR='./dir'; 7z a -mx=9 "$ARCHIVE" "$PREFIX"* "$DIR"
260
261# rar: create test archive
262# Create a RAR archive for testing
263ARCHIVE='./example/archive.rar'; PREFIX='./file'; DIR='./dir'; rar a -m5 "$ARCHIVE" "$PREFIX"* "$DIR"
264
265# tar: zstd archive from a file pattern
266# Create a zstd archive with maximum compression (through external zstd)
267ARCHIVE='./example/archive.tar.zst'; PREFIX='./file'; DIR='./dir'; COMPRESSOR='zstd -19'; tar -I "$COMPRESSOR" -cvf "$ARCHIVE" "$PREFIX"* "$DIR"Containers & Kubernetes
 1# docker network create
 2# Create a custom bridge-type Docker network
 3BRIDGE='br-monitoring'; SUBNET='SUBNET_CIDR_HERE'; GATEWAY='172.22.22.1'; NETWORK='example-network'; docker network create --opt "com.docker.network.bridge.name=$BRIDGE" --opt com.docker.network.enable_ipv6=false --driver bridge --subnet "$SUBNET" --gateway "$GATEWAY" "$NETWORK"
 4
 5# docker network connect
 6# Start a container and connect it to an existing network
 7NETWORK='swarm_network'; IMAGE='alpine'; docker run -it --rm --network "$NETWORK" "$IMAGE" sh
 8
 9# docker build image
10# Build a Docker image from a Dockerfile
11IMAGE='example/image:latest'; CONTEXT='.'; docker build -t "$IMAGE" "$CONTEXT"
12
13# docker build multiarch
14# Build a multi-architecture Docker image with Buildx
15IMAGE='example/image:latest'; PLATFORMS='linux/amd64,linux/arm64,linux/arm/v7'; CONTEXT='./'; docker buildx create --use && docker buildx build --platform "$PLATFORMS" -t "$IMAGE" "$CONTEXT"
16
17# docker multitool container
18# Start a container with network utilities using another container's resources
19CONTAINER='<CONTAINER>'; IMAGE='wbitt/network-multitool:alpine-extra'; docker run --rm -it --network="container:$CONTAINER" --pid "container:$CONTAINER" "$IMAGE" bash
20
21# docker: dive image
22# Analyze Docker image contents with Dive
23IMAGE='nginx:1.29'; docker run --rm -it -v /var/run/docker.sock:/var/run/docker.sock wagoodman/dive:latest "$IMAGE"
24
25# docker: list tags — docker.io/library/nginx
26IMAGE='docker.io/library/nginx'; skopeo list-tags "docker://$IMAGE"
27
28# docker: list tags — codeberg.org/forgejo/forgejo
29IMAGE='codeberg.org/forgejo/forgejo'; skopeo list-tags "docker://$IMAGE"
30
31# docker: list tags — ghcr.io/home-assistant/home-assistant
32IMAGE='ghcr.io/home-assistant/home-assistant'; skopeo list-tags "docker://$IMAGE"
33
34# docker: copy files from bind to volume
35VOLUME='example-volume'; DIR='./data/'; docker volume create "$VOLUME" && docker run --rm -v "$DIR:/from/:ro" -v "$VOLUME:/to/" alpine sh -c "cp -av /from/. /to/" && docker run --rm -v "$VOLUME:/data/" alpine sh -c "ls -l /data"
36
37# k8s: oidc
38kubectl oidc-login setup
39
40# k8s: get context
41kubectl config get-contexts
42
43# k8s: current context
44kubectl config current-context
45
46# k8s: switch context
47NAME='<NAME>'; CONTEXT='example-context'; kubectl config use-context "$NAME@$CONTEXT"
48
49# k8s: view config
50kubectl config view
51
52# k8s: cluster info
53kubectl cluster-info
54
55# k8s: all nodes
56kubectl get nodes -A
57
58# k8s: get objects
59# Get information about various Kubernetes objects in a namespace
60NAMESPACE='default'; kubectl -n "$NAMESPACE" get pods,svc,pvc,sts,pv -o wide
61
62# k8s: labels
63# Show labels for all Kubernetes nodes
64kubectl get nodes --show-labels
65
66# k8s: delete all
67# Force-delete all resources in the specified namespace
68NAMESPACE='NAMESPACE_HERE'; kubectl delete all --all -n "$NAMESPACE" --force --grace-period=0
69
70# k8s: validate YAML syntax
71# Check YAML manifest syntax on the client side
72MANIFEST='./example.yaml'; kubectl apply --dry-run=client -f "$MANIFEST"
73
74# k8s: validate with API server wthout changes
75# Check a manifest with the Kubernetes API server without applying changes
76MANIFEST='./example.yaml'; kubectl apply --dry-run=server -f "$MANIFEST"
77
78# helm: add repo
79# Add an external Helm chart repository
80REPO='gitea-charts'; URL='https://dl.gitea.com/charts/'; helm repo add "$REPO" "$URL"
81
82# helm: search repo
83# Search charts in the added Helm repository
84REPO='gitea-charts'; helm search repo "$REPO"
85
86# helm: download chart files
87# Download and unpack a Helm chart
88CHART='example-repo/example-chart'; helm pull "$CHART" --untarVirtual Machines
  1# qcow2: install tools
  2# Install the required tools for working with QCOW2 (qemu-utils, libguestfs-tools)
  3apt install -y qemu-utils libguestfs-tools
  4
  5# qcow2: download image
  6# Download the Debian 13 QCOW2 cloud image
  7URL='https://example.invalid/image.qcow2'; wcurl "$URL"
  8
  9# qcow2: resize image
 10# Resize a QCOW2 disk image
 11IMAGE='./example/image.qcow2'; SIZE='20G'; qemu-img resize "$IMAGE" "$SIZE"
 12
 13# qcow2: customize image
 14# Configure a QCOW2 image (update, package installation, locales)
 15IMAGE='./example/image.qcow2'; PACKAGES='qemu-guest-agent,locales,zsh,git,curl,neovim,bat,eza,fzf,grc'; virt-customize -a "$IMAGE" --update --install "$PACKAGES" --run-command "echo 'en_US.UTF-8 UTF-8' >> /etc/locale.gen" --run-command "echo 'ru_RU.UTF-8 UTF-8' >> /etc/locale.gen" --run-command "locale-gen"
 16
 17# qcow2: set permissions
 18# Set permissions and owner for a file
 19FILE='./example/file.txt'; MODE='640'; OWNER='root:'; chmod "$MODE" "$FILE" && chown "$OWNER" "$FILE"
 20
 21# qcow2: copy file to root
 22# Copy a file from the host into a QCOW2 image
 23HOST='./example.txt'; GUEST='/example/directory'; IMAGE='./example/image.qcow2'; virt-copy-in -a "$IMAGE" "$HOST" "$GUEST"
 24
 25# qcow2: edit file
 26# Edit a file inside a QCOW2 image
 27GUEST='/example/file.conf'; IMAGE='./example/image.qcow2'; virt-edit -a "$IMAGE" "$GUEST"
 28
 29# qcow2: mount image
 30# Mount a QCOW2 disk image
 31IMAGE='./example/image.qcow2'; MOUNT='./example/mount'; guestmount -i -a "$IMAGE" "$MOUNT"
 32
 33# qcow2: unmount image
 34# Unmount a QCOW2 disk image
 35MOUNT='./example/mount'; guestunmount "$MOUNT"
 36
 37# qcow2: start interactive shell
 38# Start an interactive guestfish shell for a QCOW2 image
 39IMAGE='./example/image.qcow2'; guestfish -i -a "$IMAGE"
 40
 41# qcow2: run command inside image
 42# Run a shell command inside a QCOW2 image (through guestfish)
 43# Native guestfish command: run inside guestfish, not in the shell.
 44sh 'grep root /etc/passwd'
 45
 46# qcow2: list directory contents
 47# Print directory contents inside a QCOW2 image
 48GUEST='/etc'; IMAGE='./debian-13-generic-amd64.qcow2'; virt-ls -a "$IMAGE" "$GUEST"
 49
 50# qcow2: view file content
 51# View file contents inside a QCOW2 image
 52GUEST='/etc/os-release'; IMAGE='./debian-13-generic-amd64.qcow2'; virt-cat -a "$IMAGE" "$GUEST"
 53
 54# qcow2: edit file inside image
 55GUEST='/example/file.conf'; IMAGE='./example/image.qcow2'; virt-edit -a "$IMAGE" "$GUEST"
 56
 57# qcow2: copy from host to image
 58HOST='./example.txt'; GUEST='/example/directory'; IMAGE='./example/image.qcow2'; virt-copy-in -a "$IMAGE" "$HOST" "$GUEST"
 59
 60# qcow2: copy from image to host
 61# Copy a file from a QCOW2 image to the host
 62GUEST='/etc/os-release'; HOST='./example/export'; IMAGE='./debian-13-generic-amd64.qcow2'; virt-copy-out -a "$IMAGE" "$GUEST" "$HOST"
 63
 64# qcow2: archive image content
 65# Create a tar archive from directory contents inside a QCOW2 image
 66GUEST='/etc'; ARCHIVE='./example/archive.tar'; IMAGE='./debian-13-generic-amd64.qcow2'; virt-tar-out -a "$IMAGE" "$GUEST" "$ARCHIVE"
 67
 68# qcow2: extract tar into image
 69# Extract a tar archive into a directory inside a QCOW2 image
 70GUEST='/example/directory'; IMAGE='./example/image.qcow2'; virt-tar-in -a "$IMAGE" ./archive.tar "$GUEST"
 71
 72# qcow2: show filesystems
 73# Print the list of file systems inside a QCOW2 image
 74IMAGE='./debian-13-generic-amd64.qcow2'; virt-filesystems -a "$IMAGE"
 75
 76# qcow2: extract kernel
 77# Extract the Linux kernel from a QCOW2 image
 78IMAGE='./example/image.qcow2'; virt-get-kernel -a "$IMAGE"
 79
 80# qcow2: read system logs
 81# Read system logs from a QCOW2 image
 82IMAGE='./debian-13-generic-amd64.qcow2'; virt-log -a "$IMAGE"
 83
 84# qcow2: inspect OS
 85# Get information about the operating system inside a QCOW2 image
 86IMAGE='./debian-13-generic-amd64.qcow2'; virt-inspector -a "$IMAGE"
 87
 88# qcow2: show disk usage
 89# Show disk space usage inside a QCOW2 image
 90IMAGE='./debian-13-generic-amd64.qcow2'; virt-df -a "$IMAGE"
 91
 92# qcow2: build VM image
 93# Create a virtual machine image with virt-builder
 94OS='OS_NAME_HERE'; virt-builder "$OS"
 95
 96# qcow2: manage builder repo
 97# Manage the image repository for virt-builder
 98virt-builder-repository
 99
100# qcow2: customize image (example)
101# Configure a QCOW2 image (package installation, adding an SSH key)
102IMAGE='./example/image.qcow2'; PACKAGES='vim'; NAME='root'; KEY='./example/id_ed25519.pub'; virt-customize -a "$IMAGE" --install "$PACKAGES" --ssh-inject "$NAME:file:$KEY"
103
104# qcow2: seal image
105# Prepare a QCOW2 image for deployment (cleanup, zeroing)
106IMAGE='./example/image.qcow2'; virt-sysprep -a "$IMAGE"
107
108# qcow2: sparsify image
109# Reduce the size of a QCOW2 image by removing empty blocks
110OUTPUT='./example/output.qcow2'; IMAGE='./debian-13-generic-amd64.qcow2'; virt-sparsify "$IMAGE" "$OUTPUT"
111
112# qcow2: resize partitions
113# Resize partitions inside a QCOW2 image
114INPUT='./example-input.qcow2'; OUTPUT='./example/output.qcow2'; PARTITION='/dev/sda1'; virt-resize --expand "$PARTITION" "$INPUT" "$OUTPUT"
115
116# qm: 1-install required tools
117# Install libguestfs-tools for managing images in Proxmox
118apt update && apt install -y libguestfs-tools
119
120# qm: 2-download Deb13 qcow2 image
121# Download the Debian 13 QCOW2 cloud image
122URL='https://example.invalid/image.qcow2'; wcurl "$URL"
123
124# qm: 3-resize image
125# Resize a QCOW2 image for use in Proxmox
126IMAGE='./example/image.qcow2'; SIZE='20G'; qemu-img resize "$IMAGE" "$SIZE"
127
128# qm: 3-create VM
129# Create a new virtual machine in Proxmox
130VMID='VM_ID_HERE'; NAME='debian13-k8s-template'; MEMORY='2048'; CORES='2'; BRIDGE='vmbr0'; qm create "$VMID" --name "$NAME" --memory "$MEMORY" --cores "$CORES" --net0 "virtio,bridge=$BRIDGE"
131
132# qm: 4-import disk
133# Import a QCOW2 image as a disk for a Proxmox VM
134STORAGE='<STORAGE>'; VMID='VM_ID_HERE'; IMAGE='./debian-13-generic-amd64.qcow2'; qm importdisk "$VMID" "$IMAGE" "$STORAGE" --format qcow2
135
136# qm: 5-attach SCSI disk
137# Attach the imported disk to the VM as a SCSI device
138STORAGE='<STORAGE>'; VMID='VM_ID_HERE'; qm set "$VMID" --scsihw virtio-scsi-single --scsi0 "$STORAGE:$VMID/vm-$VMID-disk-0.qcow2"
139
140# qm: 6-set boot order
141# Set the Proxmox VM boot order
142VMID='VM_ID_HERE'; DISK='scsi0'; qm set "$VMID" --boot "order=$DISK"
143
144# qm: 7-add cloud-init disk
145# Add a virtual disk for Cloud-Init to the VM
146STORAGE='<STORAGE>'; VMID='VM_ID_HERE'; qm set "$VMID" --ide0 "$STORAGE:cloudinit"
147
148# qm: 8-enable serial console
149# Enable serial console for the Proxmox VM
150VMID='VM_ID_HERE'; qm set "$VMID" --serial0 socket --vga serial0
151
152# qm: 9-enable guest agent
153# Enable QEMU Guest Agent for the VM
154VMID='VM_ID_HERE'; qm set "$VMID" --agent enabled=1
155
156# qm: 10-convert to template
157# Convert the Proxmox VM to a template
158VMID='VM_ID_HERE'; qm template "$VMID"
159
160# qm: 11-rescan VM
161# Rescan the Proxmox VM configuration
162VMID='VM_ID_HERE'; qm rescan --vmid "$VMID"
163
164# qm: 12-show config
165# Show the full Proxmox VM configuration
166VMID='VM_ID_HERE'; qm config "$VMID"
167
168# proxmox: add role
169# Add a new user role in Proxmox (pveum)
170ROLE='<ROLE>'; PRIVILEGES='Pool.Allocate VM.Console VM.Allocate VM.Clone VM.Config.CDROM VM.Config.CPU VM.Config.Cloudinit VM.Config.Disk VM.Config.HWType VM.Config.Memory VM.Config.Network VM.Config.Options VM.Audit VM.PowerMgmt VM.GuestAgent.Audit Datastore.AllocateSpace Datastore.Allocate Datastore.Audit SDN.Use'; pveum role add "$ROLE" -privs "$PRIVILEGES"
171
172# proxmox: add user
173# Add a new user in Proxmox (pveum)
174USERID='<USERID>'; pveum user add "$USERID"
175
176# proxmox: assign role to puser
177# Assign a role to a Proxmox user
178ACL='/vms/VM_ID_HERE'; USERID='<USERID>'; ROLE='<ROLE>'; pveum aclmod "$ACL" -user "$USERID" -role "$ROLE"
179
180# proxmox: create API token
181# Create an API token for a Proxmox user
182USERID='<USERID>'; TOKEN='<TOKEN>'; PRIVSEP='0'; pveum user token add "$USERID" "$TOKEN" --privsep "$PRIVSEP"
183
184# proxmox: list VM from all nodes
185pvesh get /cluster/resources --type vm
186
187# proxmox: list VM from all nodes (selected fields)
188pvesh get /cluster/resources --type vm --output-format json | jq -r '.[] | select(.type == "qemu") | "Node: \(.node); VMID: \(.vmid); Name: \(.name); Status: \(.status);"' | column -t -s ';'
189
190# proxmox: list VM from all nodes (selected fields with grep/sort)
191PATTERN='infra.*prod'; pvesh get /cluster/resources --type vm --output-format json | jq -r '.[] | select(.type == "qemu") | "Node: \(.node); VMID: \(.vmid); Name: \(.name); Status: \(.status);"' | grep -E "$PATTERN" | sort -h -t'-' -k 2,2 | column -t -s ';'
192
193# cloudinit: clean and init
194cloud-init clean && cloud-init initDevelopment & Automation
  1# git: init repo
  2# Initialize a new Git repository and add the remote origin
  3URL='https://example.invalid/example/repository.git'; BRANCH='main'; git init --initial-branch="$BRANCH" && git remote add origin "$URL"
  4
  5# git: init with config
  6# Initialize a Git repository with user and origin configuration
  7URL='https://example.invalid/example/repository.git'; BRANCH='main'; NAME='Ivan Cherniy'; EMAIL='kar-kar@r4ven.me'; git init --initial-branch="$BRANCH" && git config user.name "$NAME" && git config user.email "$EMAIL" && git remote add origin "$URL"
  8
  9# git: push changes
 10# Add, commit, and push changes to the remote repository
 11FILE='./example-file.txt'; MESSAGE='upd'; git add "$FILE" && git commit -m "$MESSAGE" && git push
 12
 13# git: git log visual
 14# Show a nice graphical Git log
 15git log --pretty=format:"%h %ad | %s%d [%an]" --graph --date=short
 16
 17# git: create keep files
 18# Create .gitkeep files in empty repository directories
 19DIR='./example-repo'; find "$DIR" -type d -empty -exec touch {}/.gitkeep \;
 20
 21# curl: telegream message
 22# Send a text message to Telegram through the Bot API
 23TOKEN='BOT_TOKEN_HERE'; CHAT='CHAT_ID_HERE'; ITEM='Example item'; MESSAGE='Example message'; API='https://api.telegram.org'; curl -s -X POST --data-urlencode "chat_id=$CHAT" --data-urlencode "text=$ITEM: $MESSAGE" --data-urlencode "parse_mode=Markdown" "$API/bot$TOKEN/sendMessage"
 24
 25# curl: telegram file
 26# Send a file to Telegram through the Bot API
 27TOKEN='BOT_TOKEN_HERE'; CHAT='CHAT_ID_HERE'; FILE='./example/file.txt'; CAPTION='Example caption'; API='https://api.telegram.org'; curl -s -X POST --form-string "chat_id=$CHAT" -F "document=@$FILE" --form-string "caption=$CAPTION" --form-string "parse_mode=Markdown" "$API/bot$TOKEN/sendDocument"
 28
 29# curl: jenkins git generic webhook
 30# Trigger a generic Jenkins webhook for a Git event
 31URL='https://example.invalid/webhook'; BODY='{"ref":"refs/heads/main","repository":{"full_name":"test/repo"}}'; curl -L -X POST -H "Content-Type: application/json" -d "$BODY" "$URL"
 32
 33# ansible: list inventory
 34# Print the current Ansible inventory
 35ansible-inventory --list
 36
 37# ansible: get facts
 38# Gather system facts for the specified host
 39HOSTS='debian12-vpn'; FILTER='os_family,distribution_version'; ansible "$HOSTS" -m setup -a "filter=$FILTER"
 40
 41# ansible: run with vars
 42# Run an Ansible playbook with extra variables
 43PLAYBOOK='./example/playbook.yml'; VARS='user_name=root user_home=/root'; ansible-playbook "$PLAYBOOK" -e "$VARS"
 44
 45# ansible: run shell cmd
 46# Run a shell command on a remote host through Ansible
 47HOSTS='example-host'; SERVICE='example.service'; ansible "$HOSTS" -b -m command -a "systemctl start $SERVICE"
 48
 49# ansible: install role with tag by url
 50ROLE='git+https://example.invalid/roles/example-role.git'; ansible-galaxy install "$ROLE"
 51
 52# ansible: check remote tcp port
 53HOSTS='host1,host2,host3*'; COMMAND='for port in 9998 999; do for host in 10.0.0.1 10.0.0.2 10.0.0.3; do timeout 1 nc -zv $host $port; done; done'; ansible -m shell -a "$COMMAND" "$HOSTS"
 54
 55# tofu: init workdir with upgrade
 56# Initialize an OpenTofu working directory with module updates
 57tofu init -upgrade
 58
 59# tofu: validate config
 60# Check OpenTofu configuration syntax and logic
 61tofu validate
 62
 63# tofu: reconfigure backend
 64# Reconfigure the OpenTofu backend with new parameters
 65STATE='./example/state.tfstate'; tofu init -reconfigure -backend-config="path=$STATE"
 66
 67# tofu: plan
 68# Generate an OpenTofu execution plan
 69VARS='./dev.tfvars'; tofu plan -var-file="$VARS"
 70
 71# tofu: plan and planfile
 72# Create an execution plan and save it to a file
 73VARS='./dev.tfvars'; PLAN='./example/plan.tfplan'; tofu plan -var-file="$VARS" -out "$PLAN"
 74
 75# tofu: view plan file
 76# View the saved OpenTofu plan file
 77PLAN='./dev.tfplan'; tofu show "$PLAN"
 78
 79# tofu: apply
 80# Apply changes described in the OpenTofu configuration
 81VARS='./example/variables.tfvars'; tofu apply -var-file="$VARS"
 82
 83# tofu: apply with parallelism
 84# Apply changes with the specified parallelism level
 85VARS='./example/variables.tfvars'; PARALLELISM='2'; tofu apply -var-file="$VARS" -parallelism="$PARALLELISM"
 86
 87# tofu: destroy
 88# Destroy all resources managed by the OpenTofu configuration
 89VARS='./example/variables.tfvars'; tofu destroy -var-file="$VARS"
 90
 91# tofu: check format
 92# Check whether OpenTofu files match standard formatting
 93tofu fmt -check
 94
 95# tofu: format
 96# Automatically format OpenTofu configuration files
 97tofu fmt
 98
 99# tofu: format recursively
100# Recursively format OpenTofu configuration files
101tofu fmt -recursive
102
103# tofu: enable debug logging
104# Enable debug logging for OpenTofu (DEBUG level)
105export TF_LOG="DEBUG"
106
107# tofu: set log path
108# Set the path for the OpenTofu log file
109LOG='tofu.log'; export TF_LOG_PATH="$LOG"
110
111# tofu: follow log
112# Follow OpenTofu logs in real time
113LOG='./tofu.log'; tail -f "$LOG"
114
115# tofu: disable logging
116# Disable OpenTofu debug logging
117unset TF_LOG TF_LOG_PATH
118
119# python: check sytnax (only)
120FILE='test.py'; python -c 'import ast,sys; ast.parse(open(sys.argv[1]).read())' "$FILE"
121
122# python: try to compile
123FILE='./test.py'; CACHE='./__pycache__/'; python -m py_compile "$FILE"; ls -l "$CACHE"Databases
 1# mongo: get replica set status
 2# Get MongoDB replica set status
 3NAME='root'; CONFIG='./example-mongo-shell.conf'; mongo -u "$NAME" -p "$(awk -F'"' '/auth/ {print $4}' "$CONFIG")" --eval "rs.status()"
 4
 5# mongo: get count of primary nodes
 6# Count primary nodes in a MongoDB replica set
 7NAME='root'; CONFIG='./example-mongo-shell.conf'; mongo --quiet -u "$NAME" -p "$(awk -F'"' '/auth/ {print $4}' "$CONFIG")" --eval "rs.status().members.filter(m => m.stateStr === 'PRIMARY').length"
 8
 9# mongo: get count of secondary nodes
10# Count secondary nodes in a MongoDB replica set
11NAME='root'; CONFIG='./example-mongo-shell.conf'; mongo --quiet -u "$NAME" -p "$(awk -F'"' '/auth/ {print $4}' "$CONFIG")" --eval "rs.status().members.filter(m => m.stateStr === 'SECONDARY').length"
12
13# mongo: get count of unhealthy nodes
14# Count unhealthy nodes in a MongoDB replica set
15NAME='root'; CONFIG='./example-mongo-shell.conf'; mongo --quiet -u "$NAME" -p "$(awk -F'"' '/auth/ {print $4}' "$CONFIG")" --eval "rs.status().members.filter(m => m.health !== 1).length"
16
17# mongo: check connection
18# Check successful connection to MongoDB and replica set status
19NAME='root'; CONFIG='./example-mongo-shell.conf'; mongo --quiet -u "$NAME" -p "$(awk -F'"' '/auth/ {print $4}' "$CONFIG")" --eval "rs.status().ok"
20
21# mongo: check deley greater than 30 sec
22# Check MongoDB replication lag (more than 30 seconds)
23NAME='root'; CONFIG='./example-mongo-shell.conf'; mongo --quiet -u "$NAME" -p "$(awk -F'"' '/auth/ {print $4}' "$CONFIG")" --eval 'var s = rs.status(); var p = s.members.find(m=>m.stateStr==="PRIMARY").optimeDate; var bad = s.members.filter(m => m.stateStr==="SECONDARY" && Math.abs(p - m.optimeDate) > 30000).length; print(bad);'
24
25# psql: create .pgpass
26# Create a .pgpass file for automatic PostgreSQL authentication
27HOST='example.invalid'; PORT='5432'; DB='example_db'; NAME='example_user'; PASSWORD='REPLACE_WITH_PASSWORD'; FILE='./example/pgpass'; (umask 077; printf '%s:%s:%s:%s:%s\n' "$HOST" "$PORT" "$DB" "$NAME" "$PASSWORD" > "$FILE" && chmod 0600 "$FILE")
28
29# psql: enter psql
30# Enter the PostgreSQL console as the postgres user
31OSUSER='postgres'; DBUSER='postgres'; sudo -u "$OSUSER" psql -U "$DBUSER"
32
33# psql: set user password
34# Set or change the PostgreSQL user password
35# Native SQL: run inside psql, not in the shell.
36ALTER USER postgres WITH PASSWORD 'your_new_password'\;👨💻And…
Don’t forget about our Telegram channel 📱 and chat
Or maybe you want to become a co-author? Then click here🔗
💬 All the best ✌️
That should be it. If not, check the logs 🙂
Comments